- contact@verticalserve.com
- Continuous compliance, proven every hour

Blog
Compliance, explained by people who run it
Playbooks and worked examples for SOC 2, SOC 1, ISO 27001, continuous monitoring and audits, shown on the demo company’s real data.
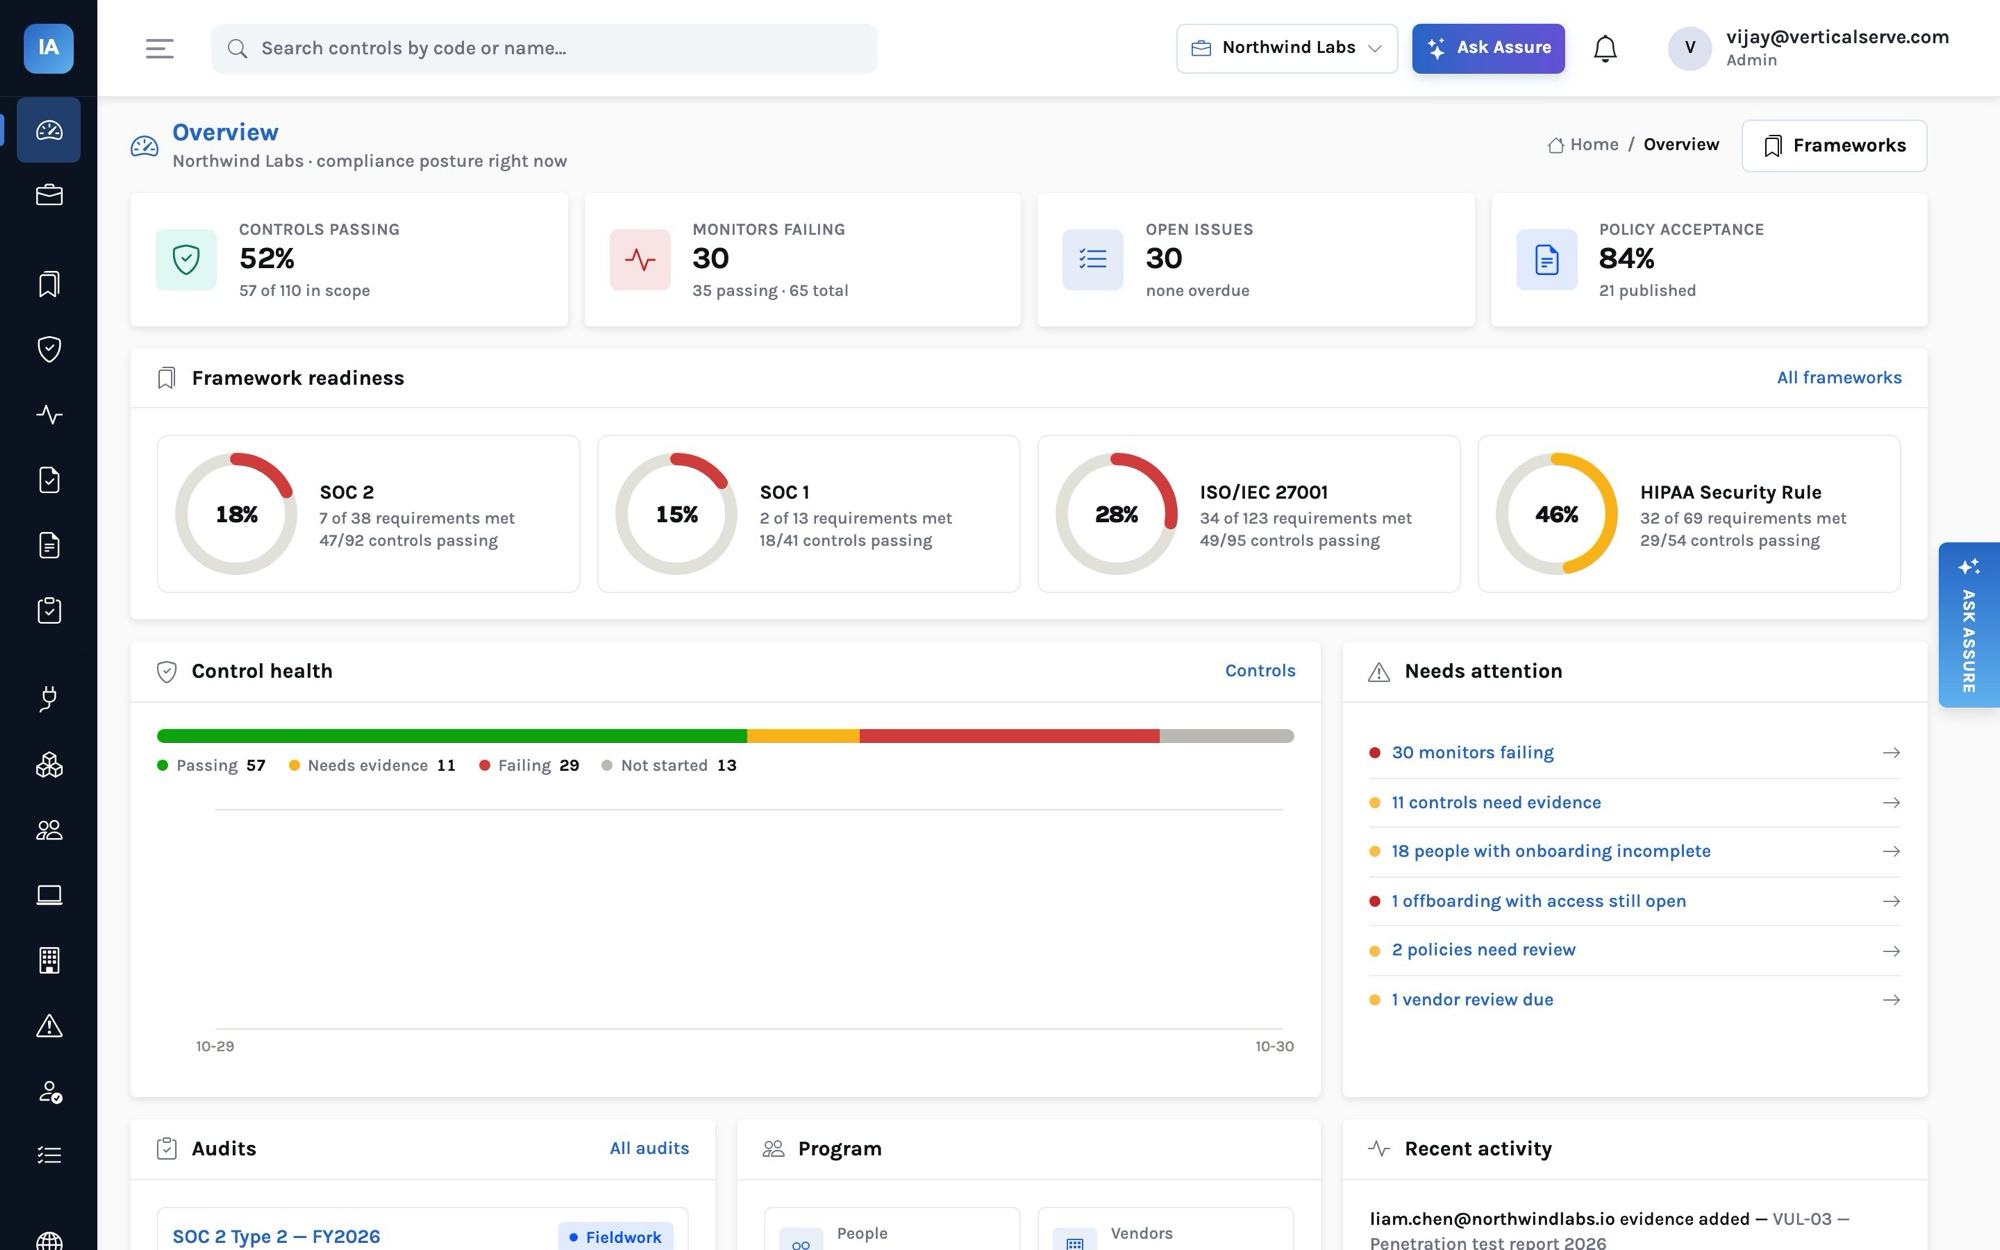
SOC 2
SOC 2 in 90 days — a practical playbook for a small SaaS team
Scope, readiness week by week, Type 1 vs Type 2, the observation period and fieldwork — a SOC 2 plan a 25-person SaaS company can actually run.
Read article
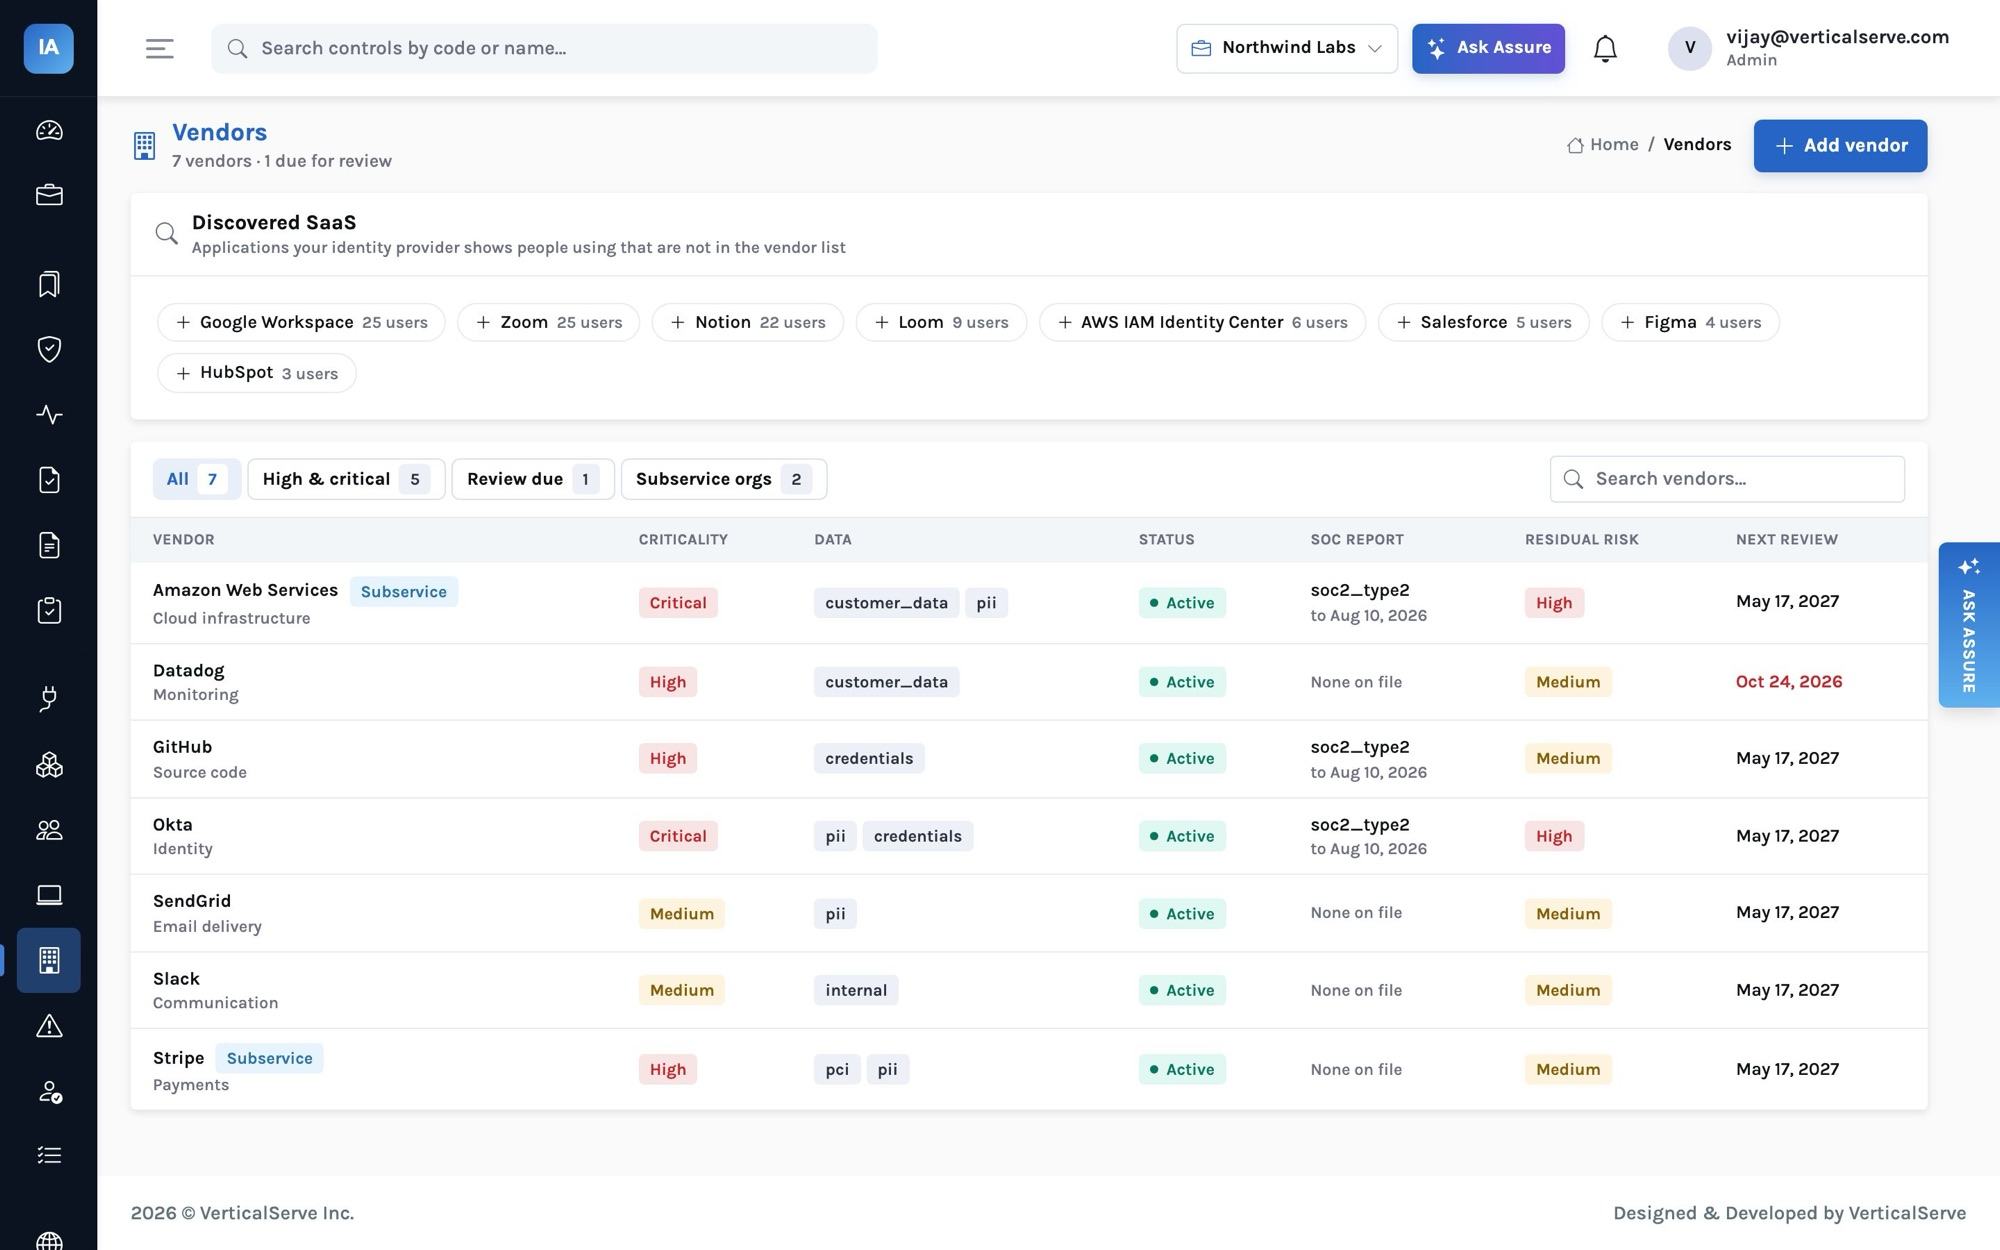
SOC 1
SOC 1 explained properly — control objectives, CUECs, CSOCs and carve-outs
How SOC 1 differs from SOC 2, how to write control objectives, and how CUECs, CSOCs and carved-out subservice organizations fit together.
Read article
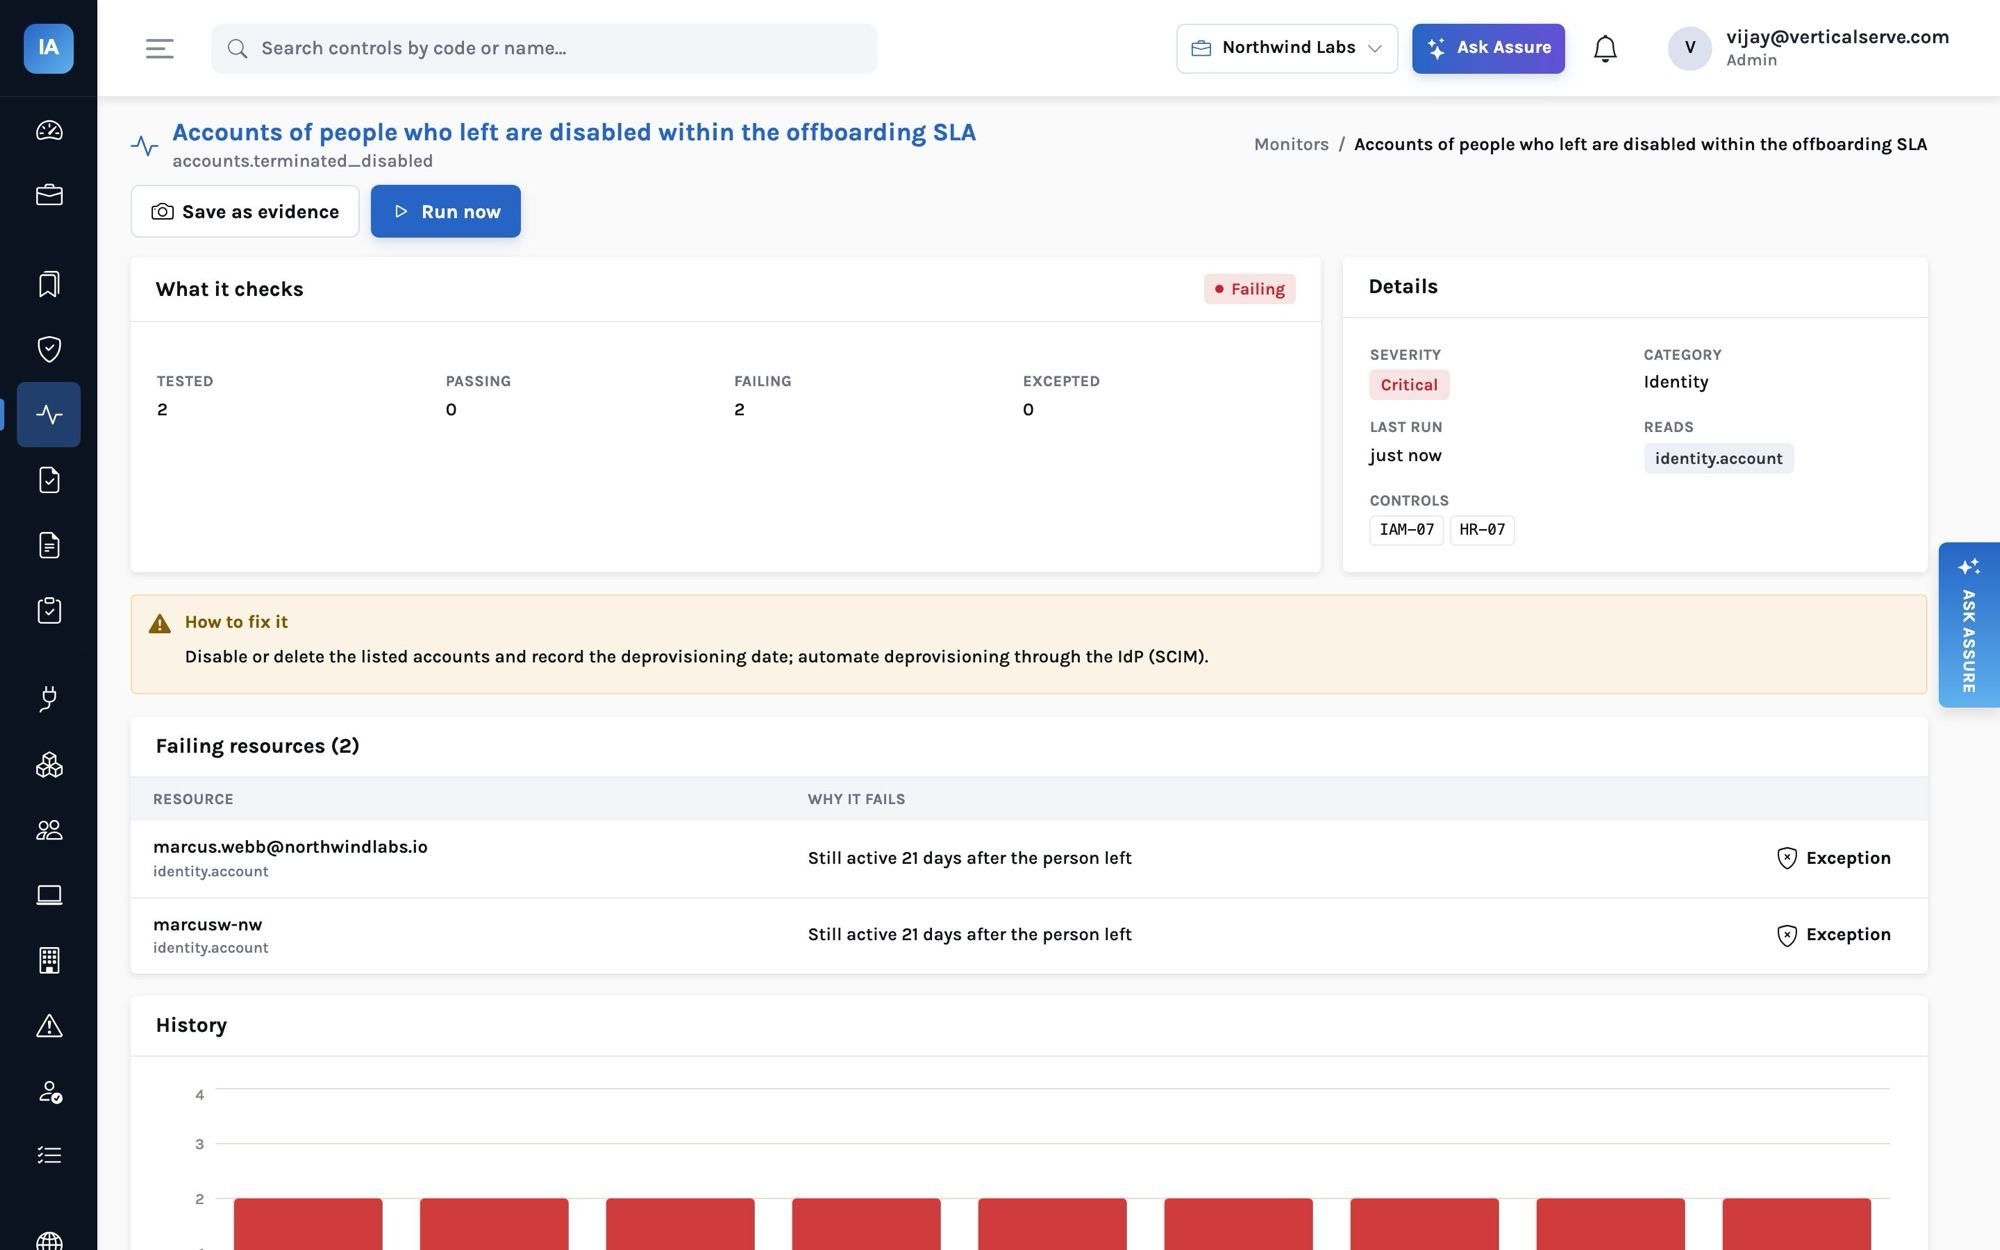
Monitoring
How continuous control monitoring actually works
From an Okta account to a framework readiness score — the data model, the 65 monitors, exceptions and the rule that keeps tests honest.
Read article
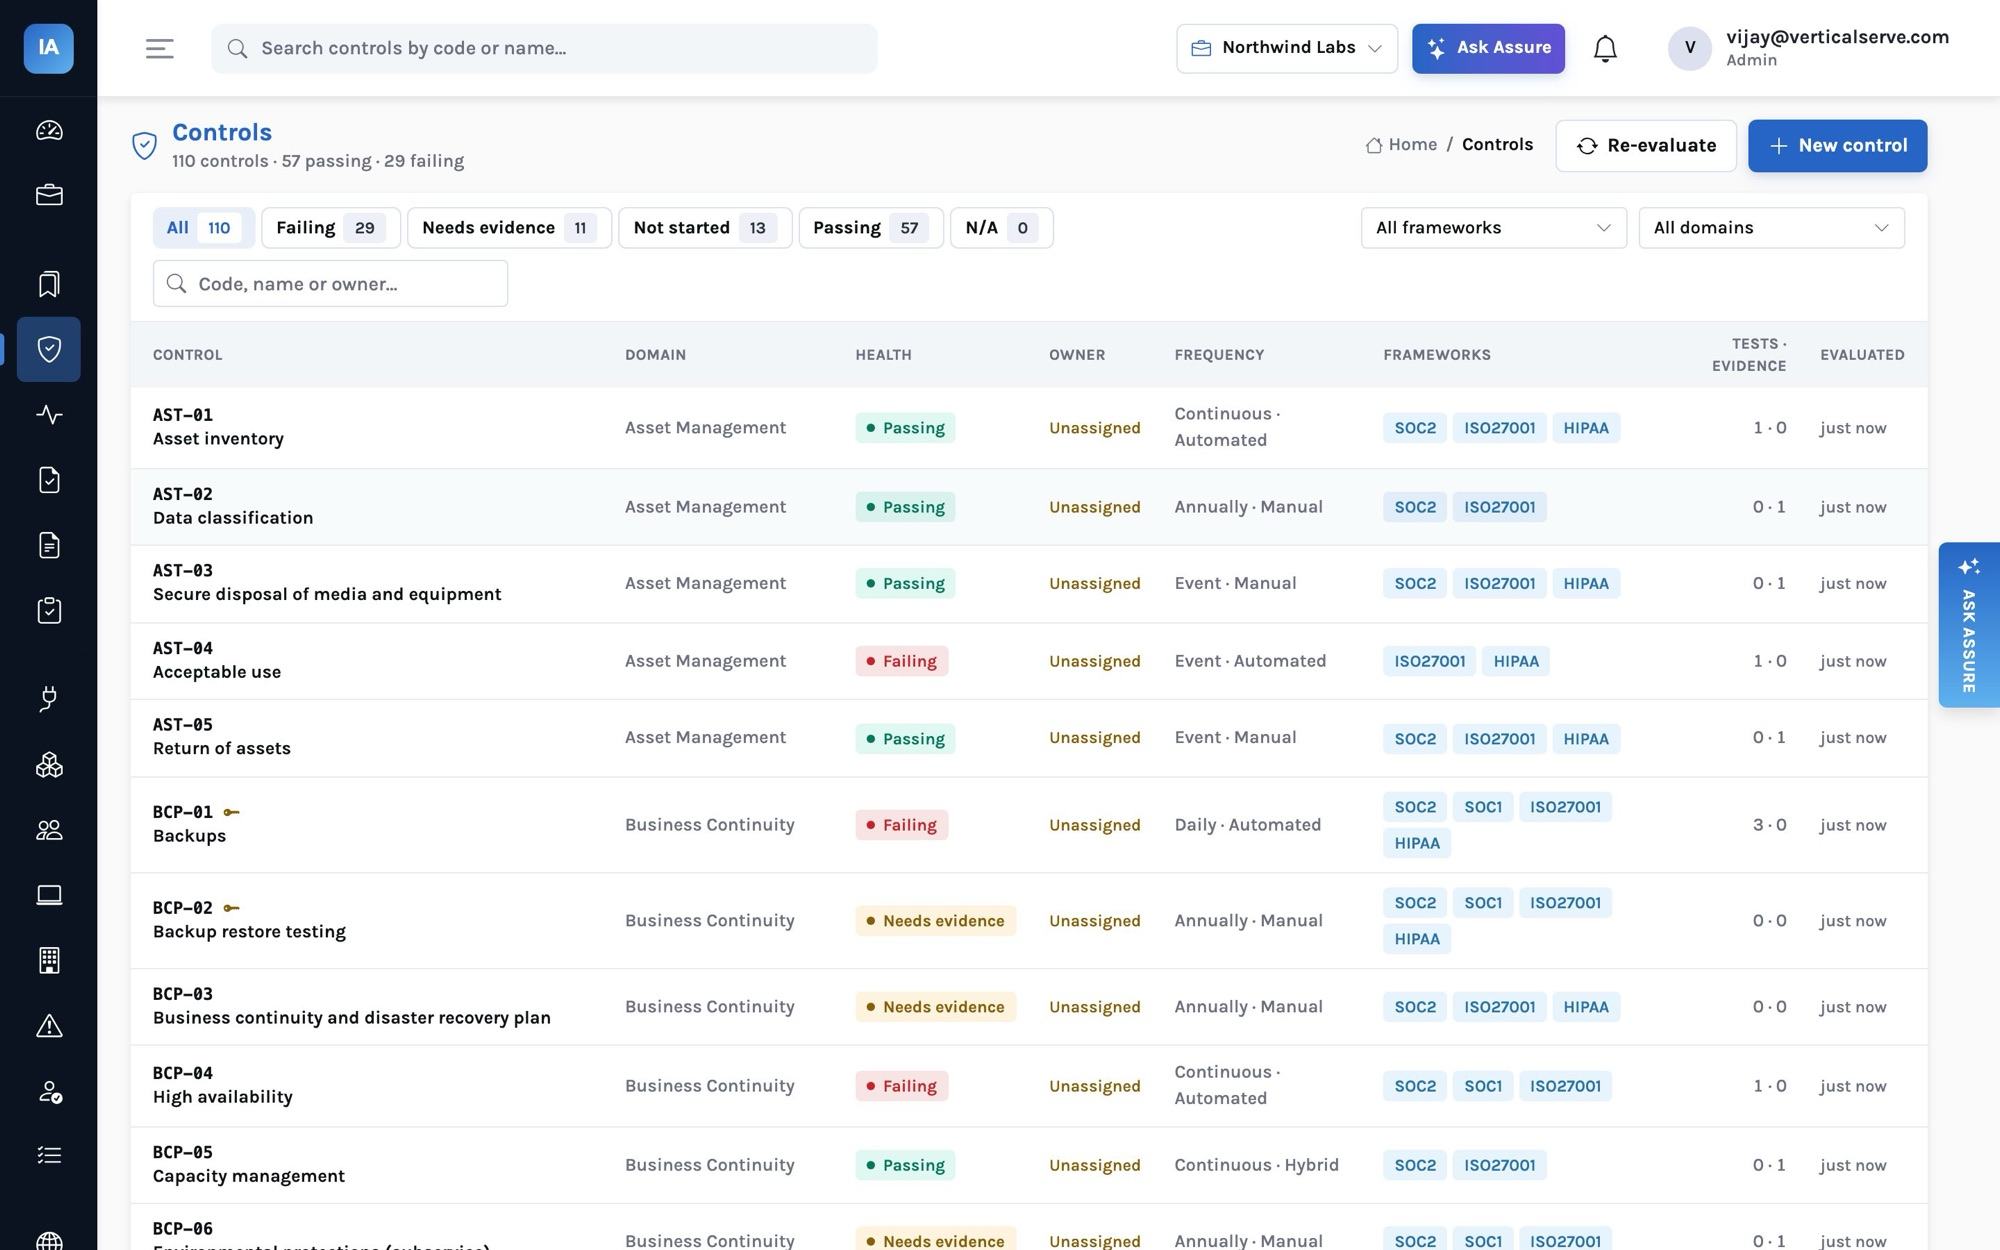
Frameworks
One control, many frameworks — cross-mapping SOC 2, ISO 27001, HIPAA, PCI DSS and more
How a unified control set lets you test MFA, code review, backups and vendor reviews once and report them to eight frameworks — with the real mappings.
Read article
Audits
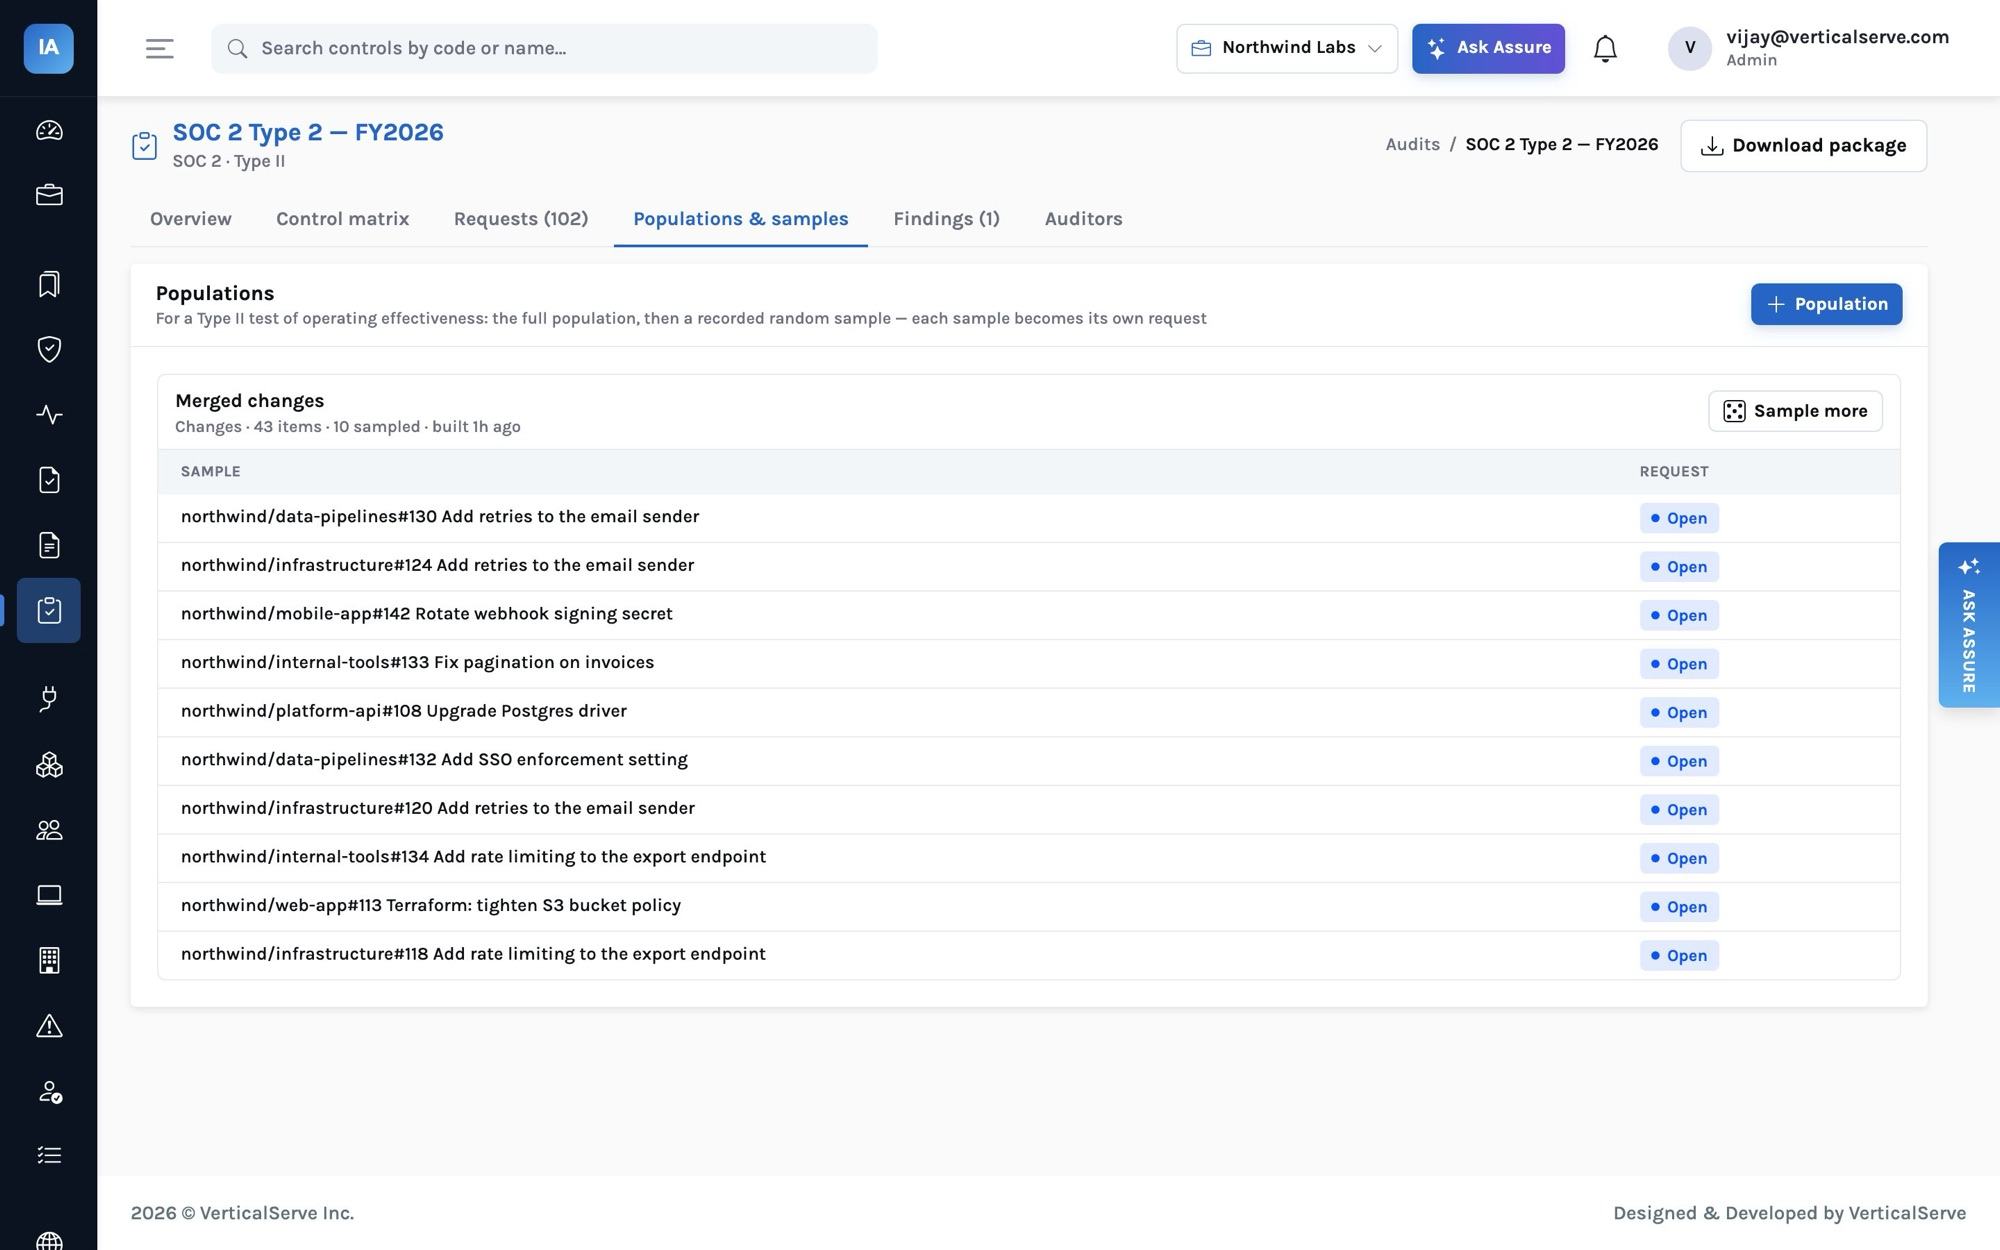
Inside a Type 2 audit — requests, populations, sampling and the auditor workspace
How fieldwork really runs — the PBC list, populations, reproducible samples, comments, findings and the audit package — with a change-management example.
Read article
Questionnaires
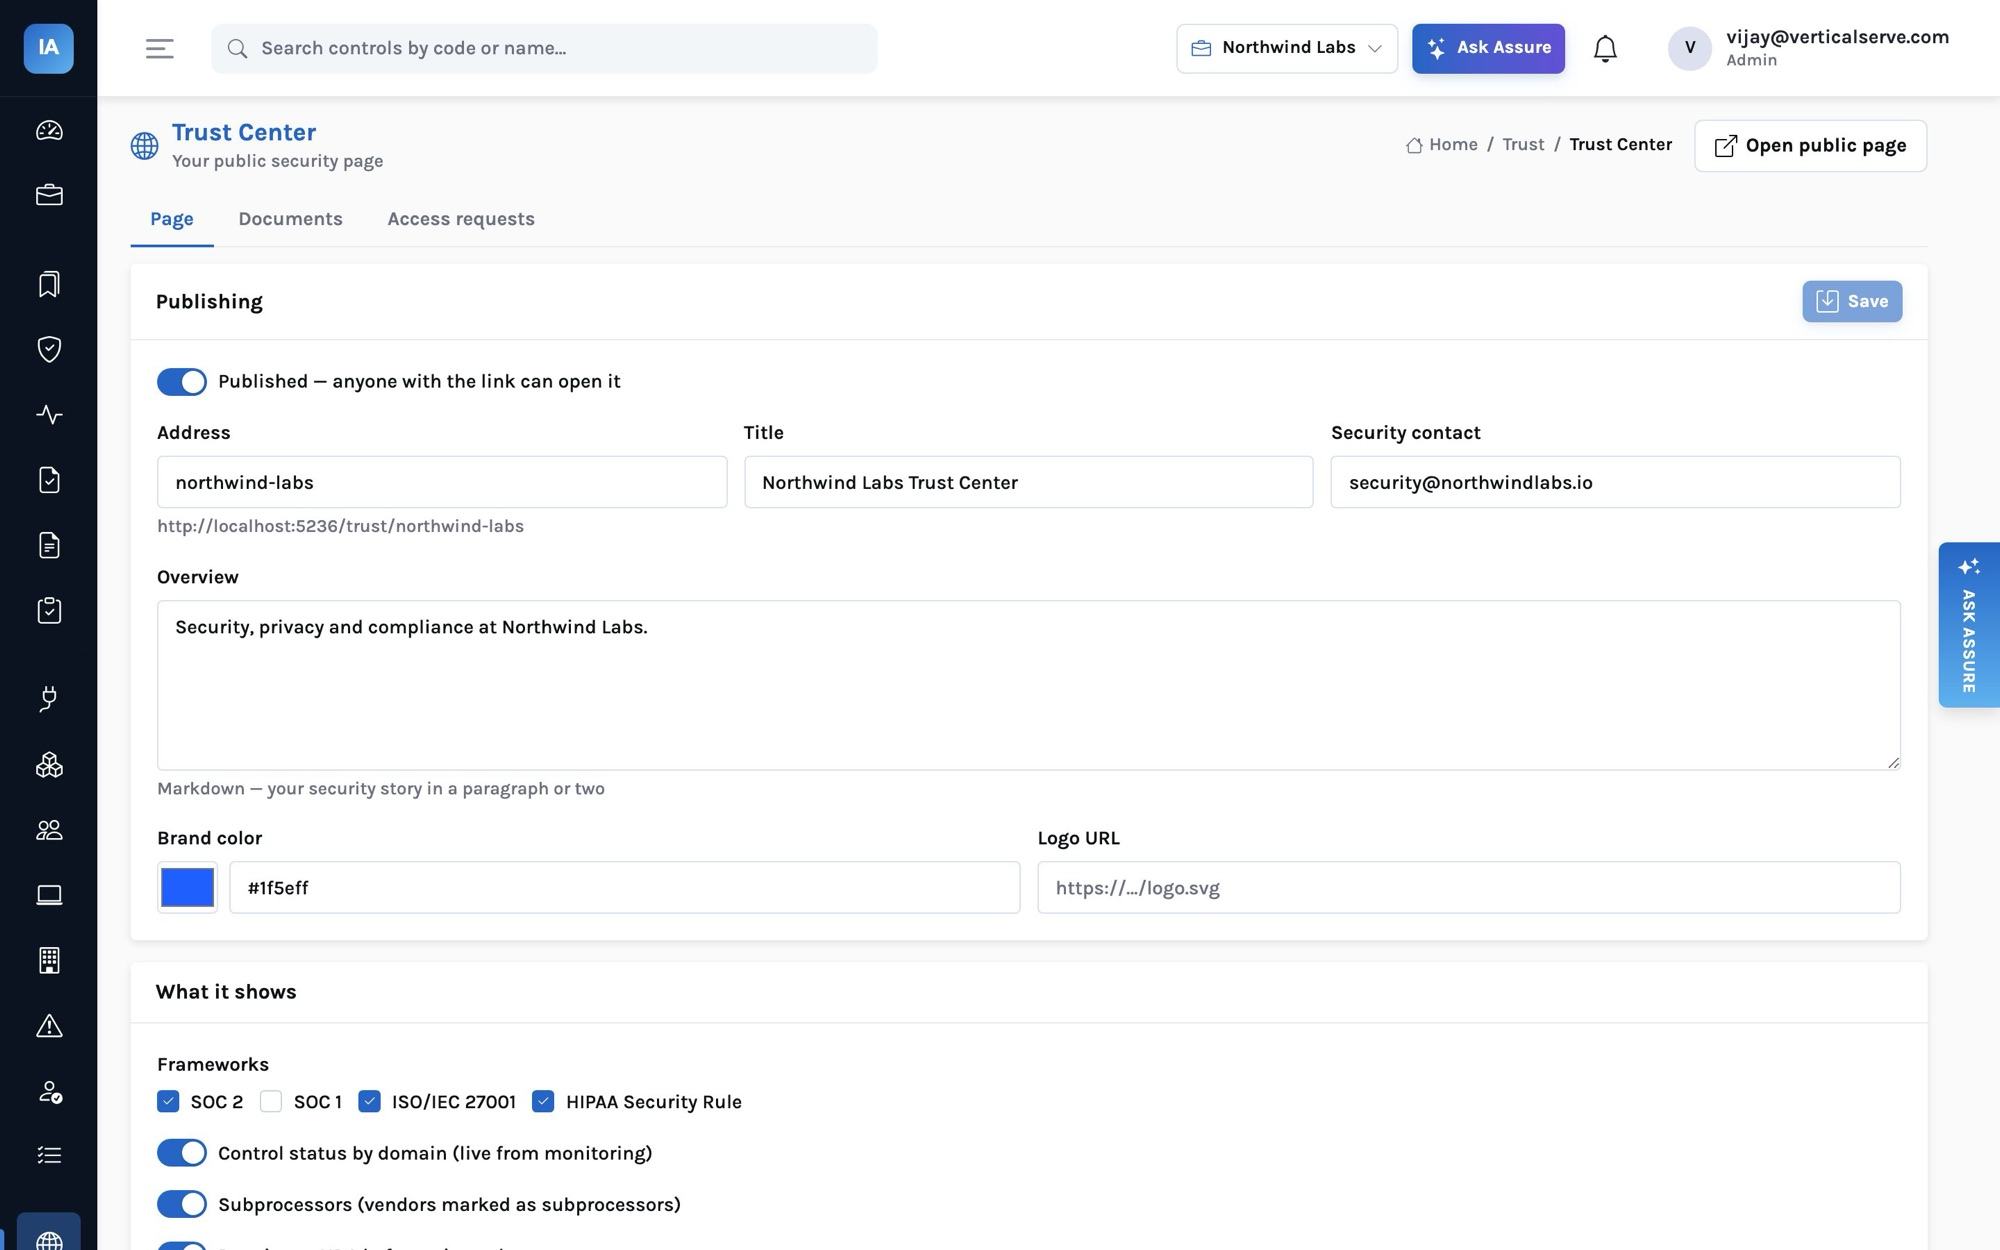
AI for security questionnaires — answers you can audit
Grounded answers with citations from your approved answers, published policies and live control health — plus a rule mode that works with no model at all.
Read article
Consultancies
Running compliance for many clients — workspaces, Portfolio and the consultant's day
How a consultancy or MSP runs many clients' SOC 2, SOC 1 and ISO programs from one place, with isolation enforced by the database itself.
Read article
Self-hosted
Self-hosted compliance — running InsightAssure in your own cloud
Why some organizations run compliance in-house — architecture, a docker compose install, sealed credentials, backups, upgrades and the agent rollout.
Read article