- contact@verticalserve.com
- Continuous compliance, proven every hour

Access reviews
Access reviews that actually remove access
Start a review for any system an integration reads. Every account comes pre-flagged, every account must be decided, and the completed review becomes evidence while revocations become issues.
The review
Every account, matched and flagged
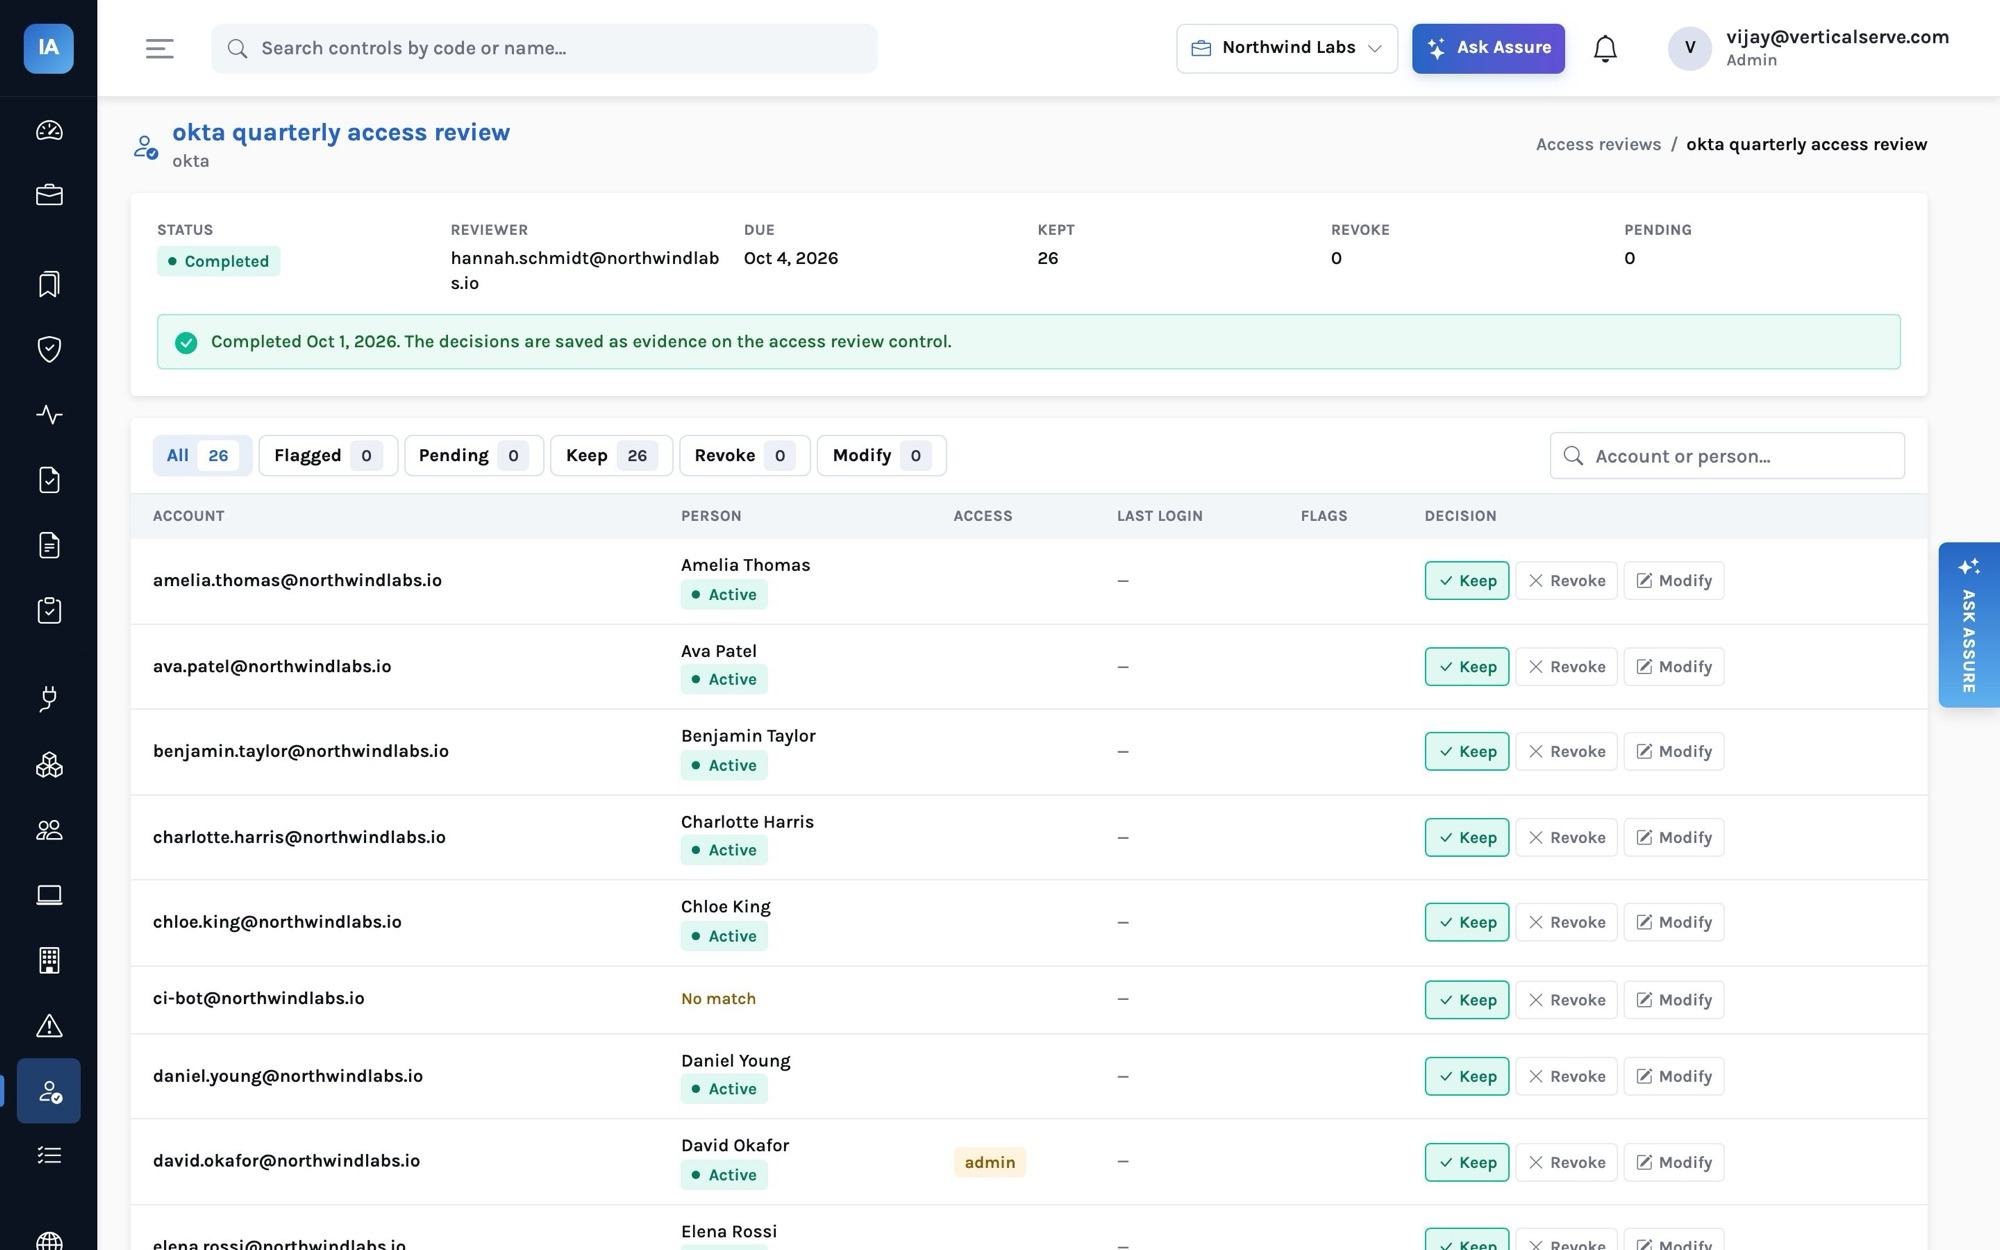
A review lists each account in the chosen system with its roles and groups, last sign-in and the person it belongs to in HR. Accounts arrive flagged:
- terminated: the person has left
- no HR record: nobody in HR matches the account (a service account, or someone who should not be there)
- admin, inactive 90 days, no MFA, disabled
The reviewer marks each one keep, revoke or modify; revoke and modify need a note saying what to change.
Completion
Evidence and remediation in one step
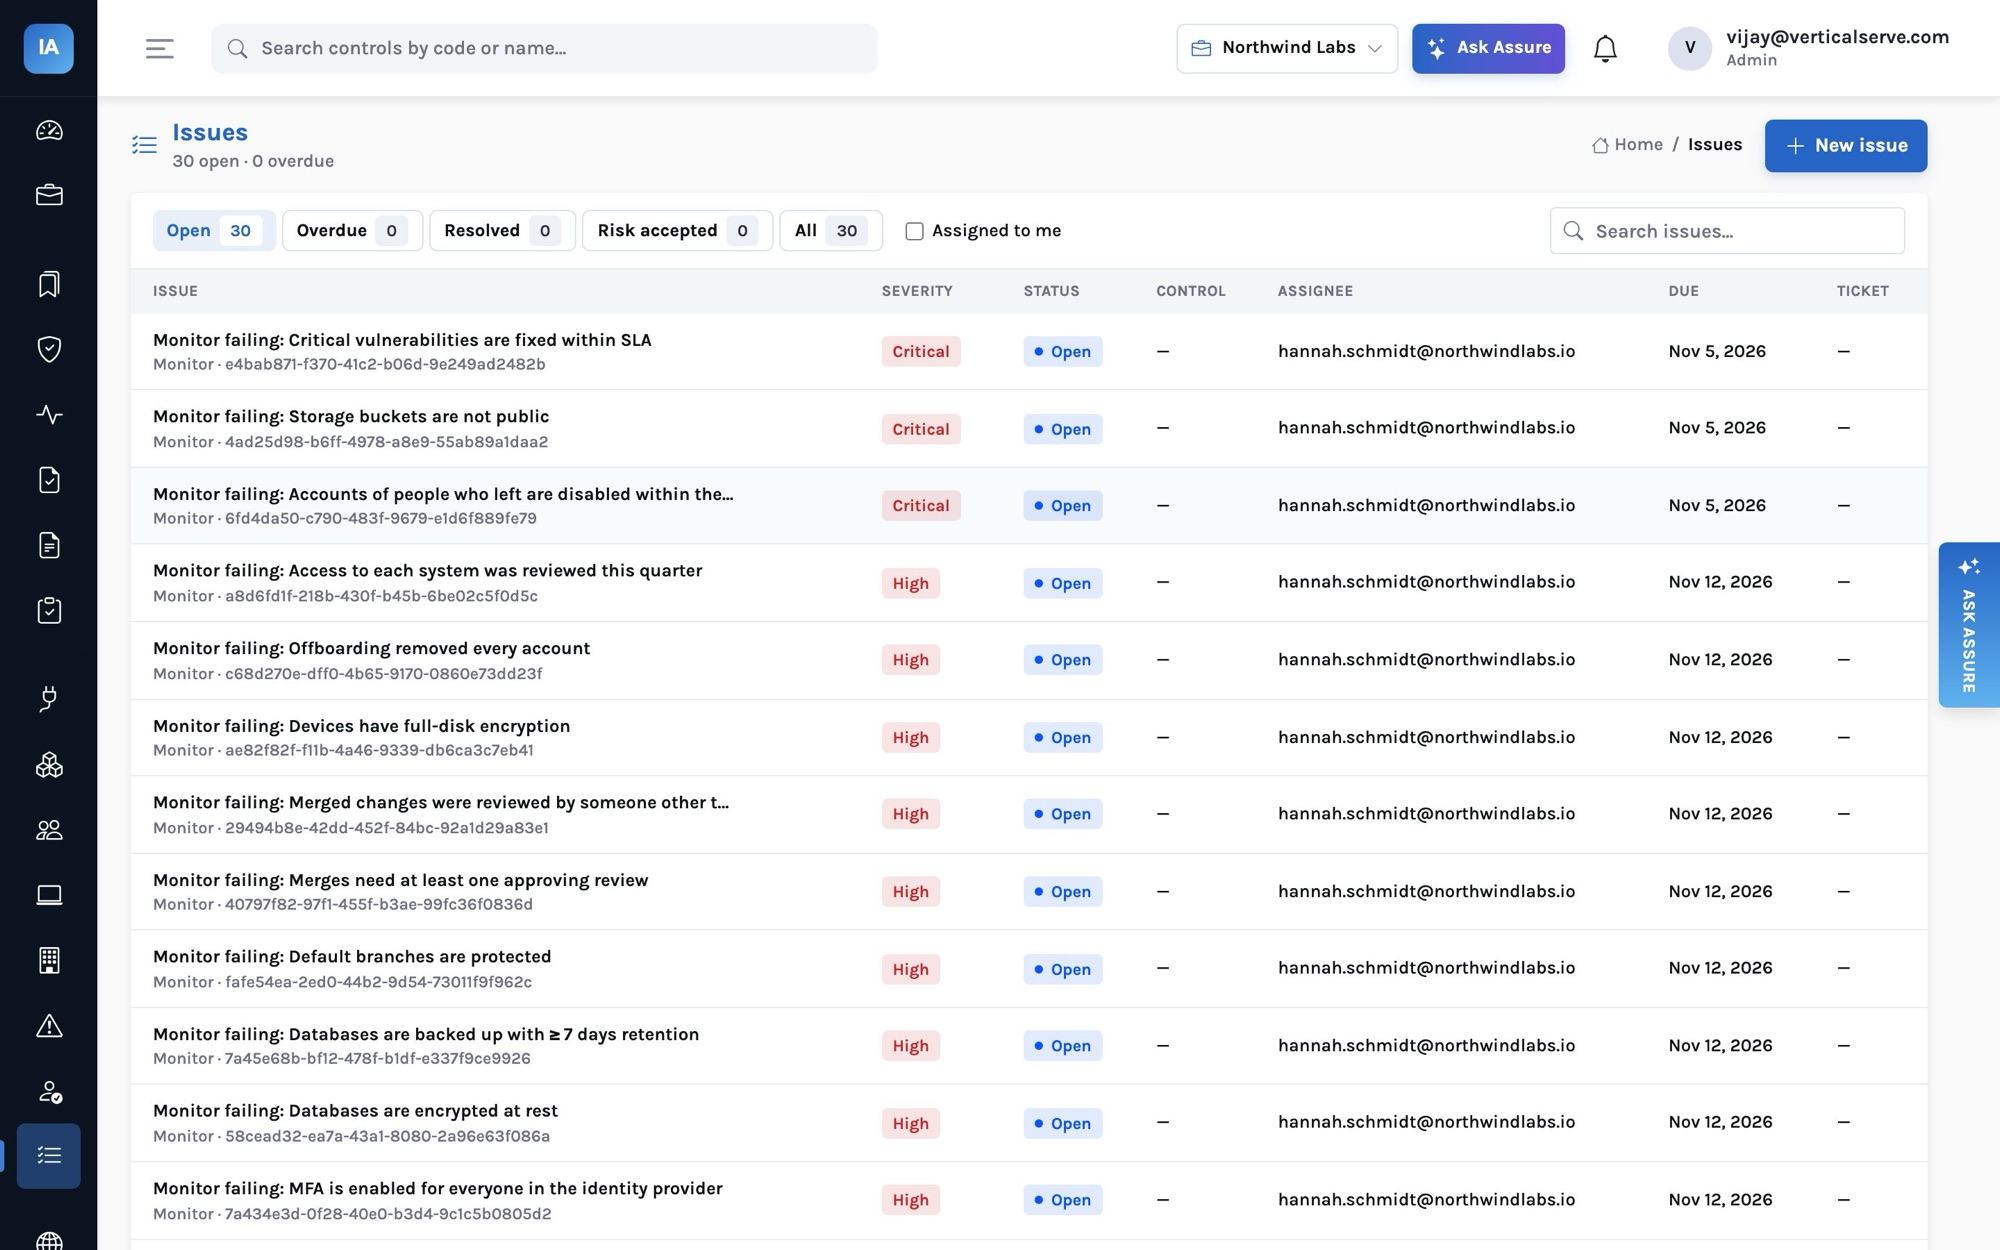
A review cannot be completed while any account is undecided. Completing it saves the decisions as evidence on IAM-05 User access reviews and IAM-06 Privileged access, and opens an issue for every revoke (high, due in 7 days) and modify. A monitor checks that every identity system was reviewed within the cadence in Settings (90 days by default).
How it works
A quarterly review from start to evidence
Questions it answers
What you can find out
Each one is answered on a screen you can open, and most can be typed into Ask Assure as they are.
Which systems are due a review?Access to each system was reviewed this quarter
Which accounts have no owner in HR?The review’s no-HR-record flag
Who has admin rights in GitHub?A GitHub review filtered to admin
Were last quarter’s revocations carried out?The access-review issues and their status
Show the auditor the Q3 Okta reviewThe review’s evidence on IAM-05
Which accounts have not signed in for 90 days?Accounts unused for 90 days are disabled
Outcomes
What teams do with it
Reviews that finish
Every account must be decided before completion.
Revocations tracked
Each one becomes an issue with an owner and a date.
Evidence without screenshots
The completed review is the evidence.
Where it stops. Reviews cover systems an integration (or the push API) reads; access inside an application that exposes no API is reviewed by uploading its user list. InsightAssure does not revoke access itself: the issue tells someone to.