- contact@verticalserve.com
- Continuous compliance, proven every hour

SOC 1
Your control objectives. Their CUECs. The cloud’s CSOCs.
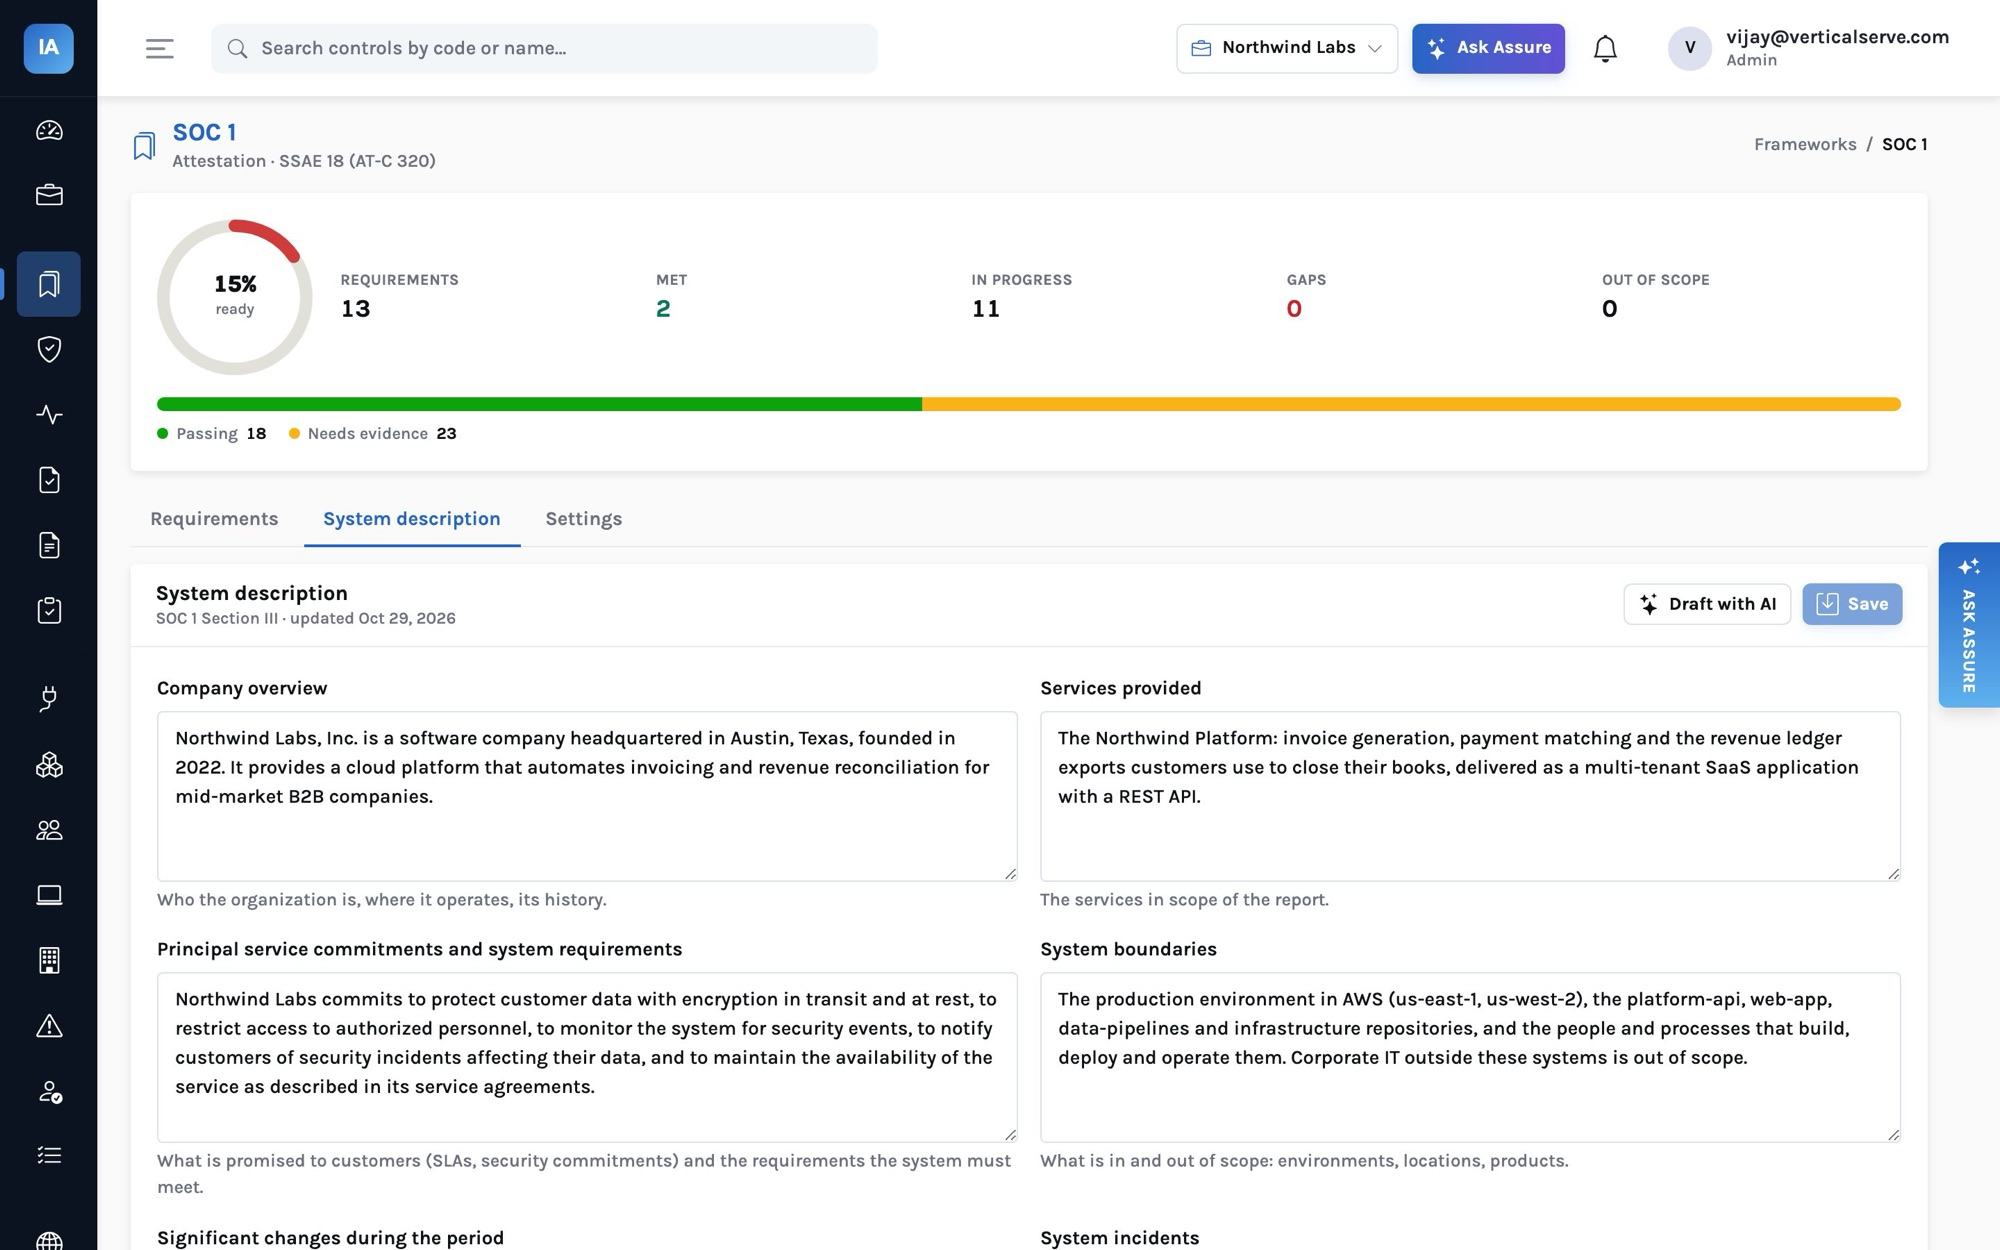
SOC 1 has no prescribed criteria: management writes the control objectives. InsightAssure makes them your own editable rows, and keeps the complementary controls on both sides of the report in the system description.
Control objectives
Thirteen to start, every one yours
The template set covers IT general controls (logical access, change management, system development, computer operations, backup and recovery, physical and environmental security, data transmission and network security, incident management, subservice organization monitoring) and business processes (client onboarding and master data, transaction input, processing, and output). Rename, rewrite, take out of scope with a reason, or add your own; each maps to unified controls like any other requirement.
Complementary controls
CUECs and CSOCs, worded the way reports word them
| What it is | Default example in InsightAssure | |
|---|---|---|
| CUEC | A control your customers (user entities) must operate for your controls to achieve their objectives | “User entities are responsible for removing access for their terminated users in a timely manner.” (CO-01) |
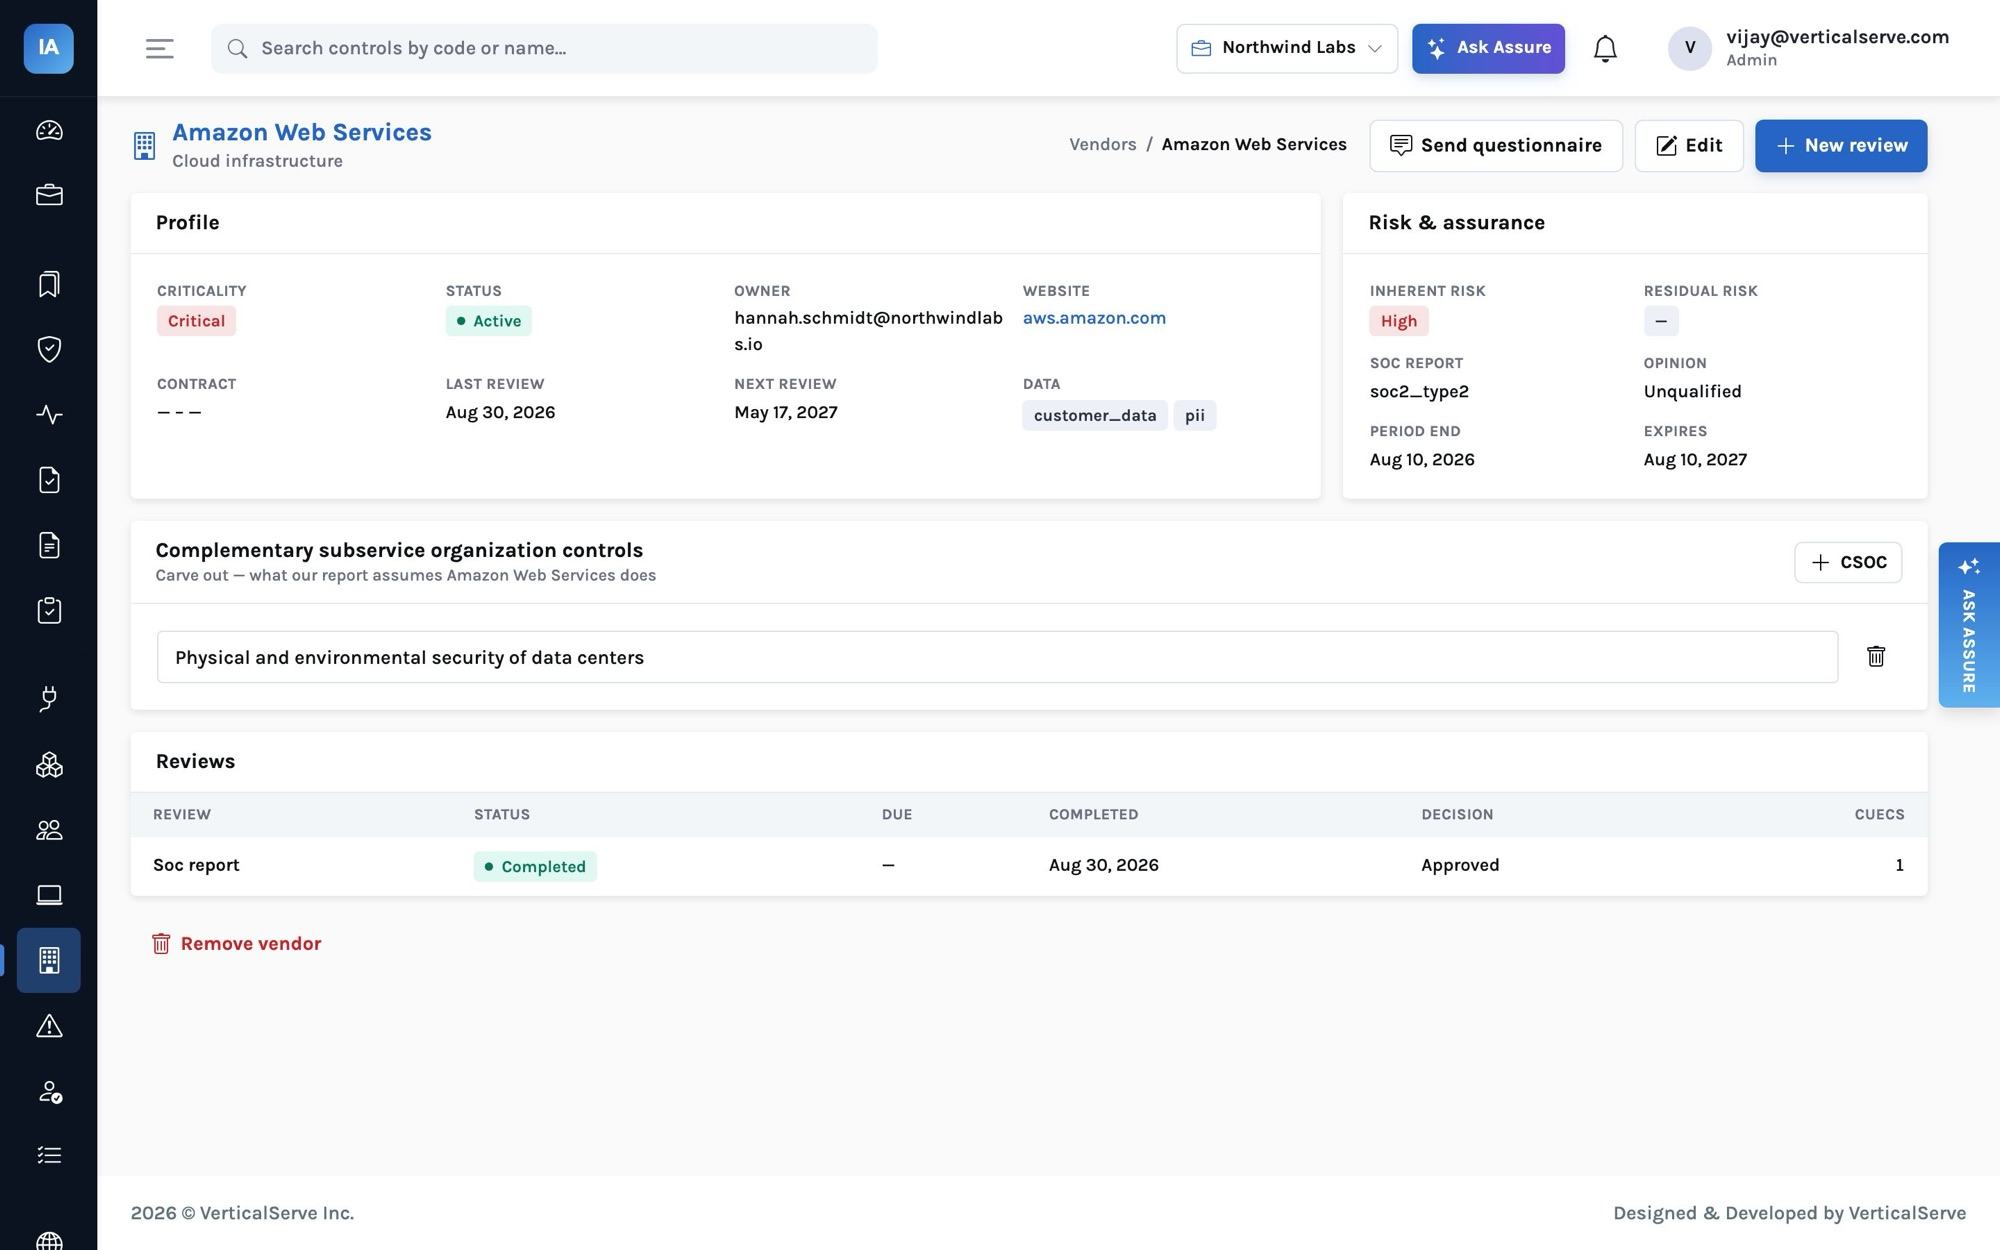
| CSOC | A control you assume a carved-out subservice organization operates | “The cloud hosting provider is responsible for restricting physical access to data center facilities… to authorized personnel.” (CO-06) |
Seven default CUECs and four default CSOCs ship with the SOC 1 template, each tied to the objectives it supports; all are editable.
Subservice organizations
Carved out, and still monitored
A vendor marked as a subservice organization records the method (carve-out or inclusive) and the CSOCs assumed of it. Its SOC report review records the opinion and expiry, and the vendors.soc_reports_current monitor fails when the report on file has expired, which is what CO-09 and VND-05 ask you to show.
How it works
Where each control sits in a SOC 1 report
Questions it answers
What you can find out
Each one is answered on a screen you can open, and most can be typed into Ask Assure as they are.
Which objectives are not yet achieved?SOC 1 requirements in progress, with their controls
What must our customers do?The system description’s CUECs
What do we assume AWS does?The CSOCs on the vendor and in the description
Is our cloud provider’s SOC report current?Subservice organizations’ SOC reports are current
Which controls are key controls?The control matrix’s Key markers
Draft our system descriptionDraft with AI from connected systems, people and vendors
Outcomes
What teams do with it
SOC 1 and SOC 2 from one program
Shared controls, separate objectives and criteria.
CUECs your customers can act on
Worded clearly, tied to objectives.
Carve-outs that hold up
Subservice reports reviewed and current.
Where it stops. The template objectives are a starting point for a technology service organization; your auditor and management decide the final wording. InsightAssure does not write the auditor’s section IV or the opinion.