- contact@verticalserve.com
- Continuous compliance, proven every hour

For consultancies
Run every client’s program from one login
Built for VerticalServe’s own model: a workspace per client, consultants holding a role in each one they support, and a portfolio that shows every client’s readiness, failing controls and audits in one place.
Portfolio
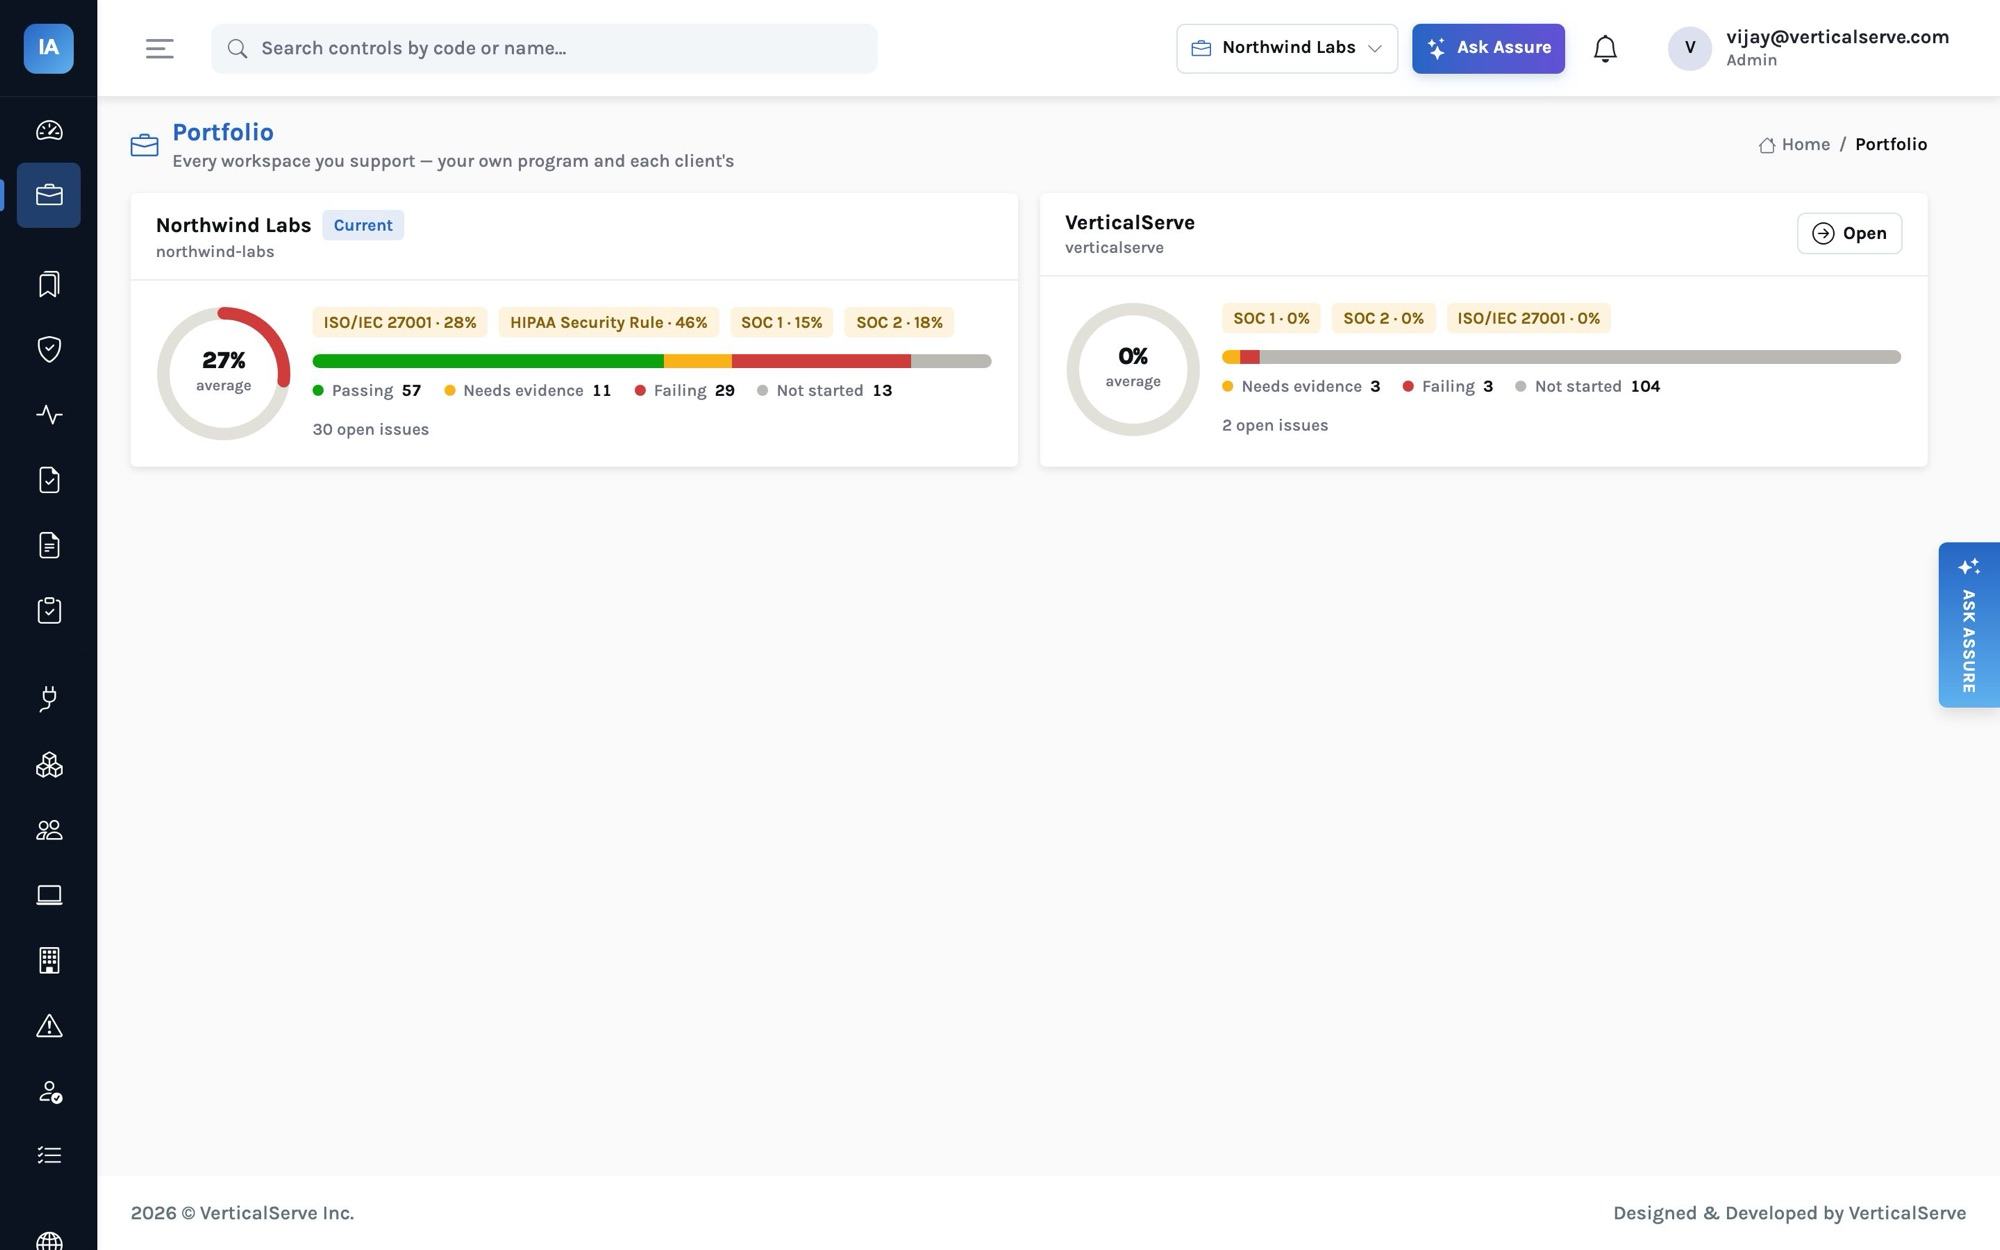
Every workspace you support, side by side
The portfolio lists each workspace your email has an account in, with your roles there, readiness per framework, control health, open and critical issues, and audits in flight. Open one and the workspace switcher signs you in to it, with the same email and that workspace’s role.
Roles
Who does what in a client’s workspace
| Role | May |
|---|---|
| admin | Everything, including users, integrations and settings |
| compliance | Run the program: frameworks, controls, policies, evidence, vendors, risks, audits, Trust Center |
| contributor | Work what is assigned: controls, issues, evidence and access-review items; read the rest |
| employee | The employee portal only |
| auditor | Only the audits they are invited to |
| viewer | Read |
Isolation
Each client’s data stays in its workspace
Every row carries its organization and every query is scoped to the caller’s; underneath, Postgres row-level security enforces the same boundary, and the application connects as an ordinary database role so the policy binds. A guessed id from another client answers 404.
A client that needs its data in its own environment runs the self-hosted edition; consultants then get accounts there instead.
How it works
Onboarding a new client in a day
Questions it answers
What you can find out
Each one is answered on a screen you can open, and most can be typed into Ask Assure as they are.
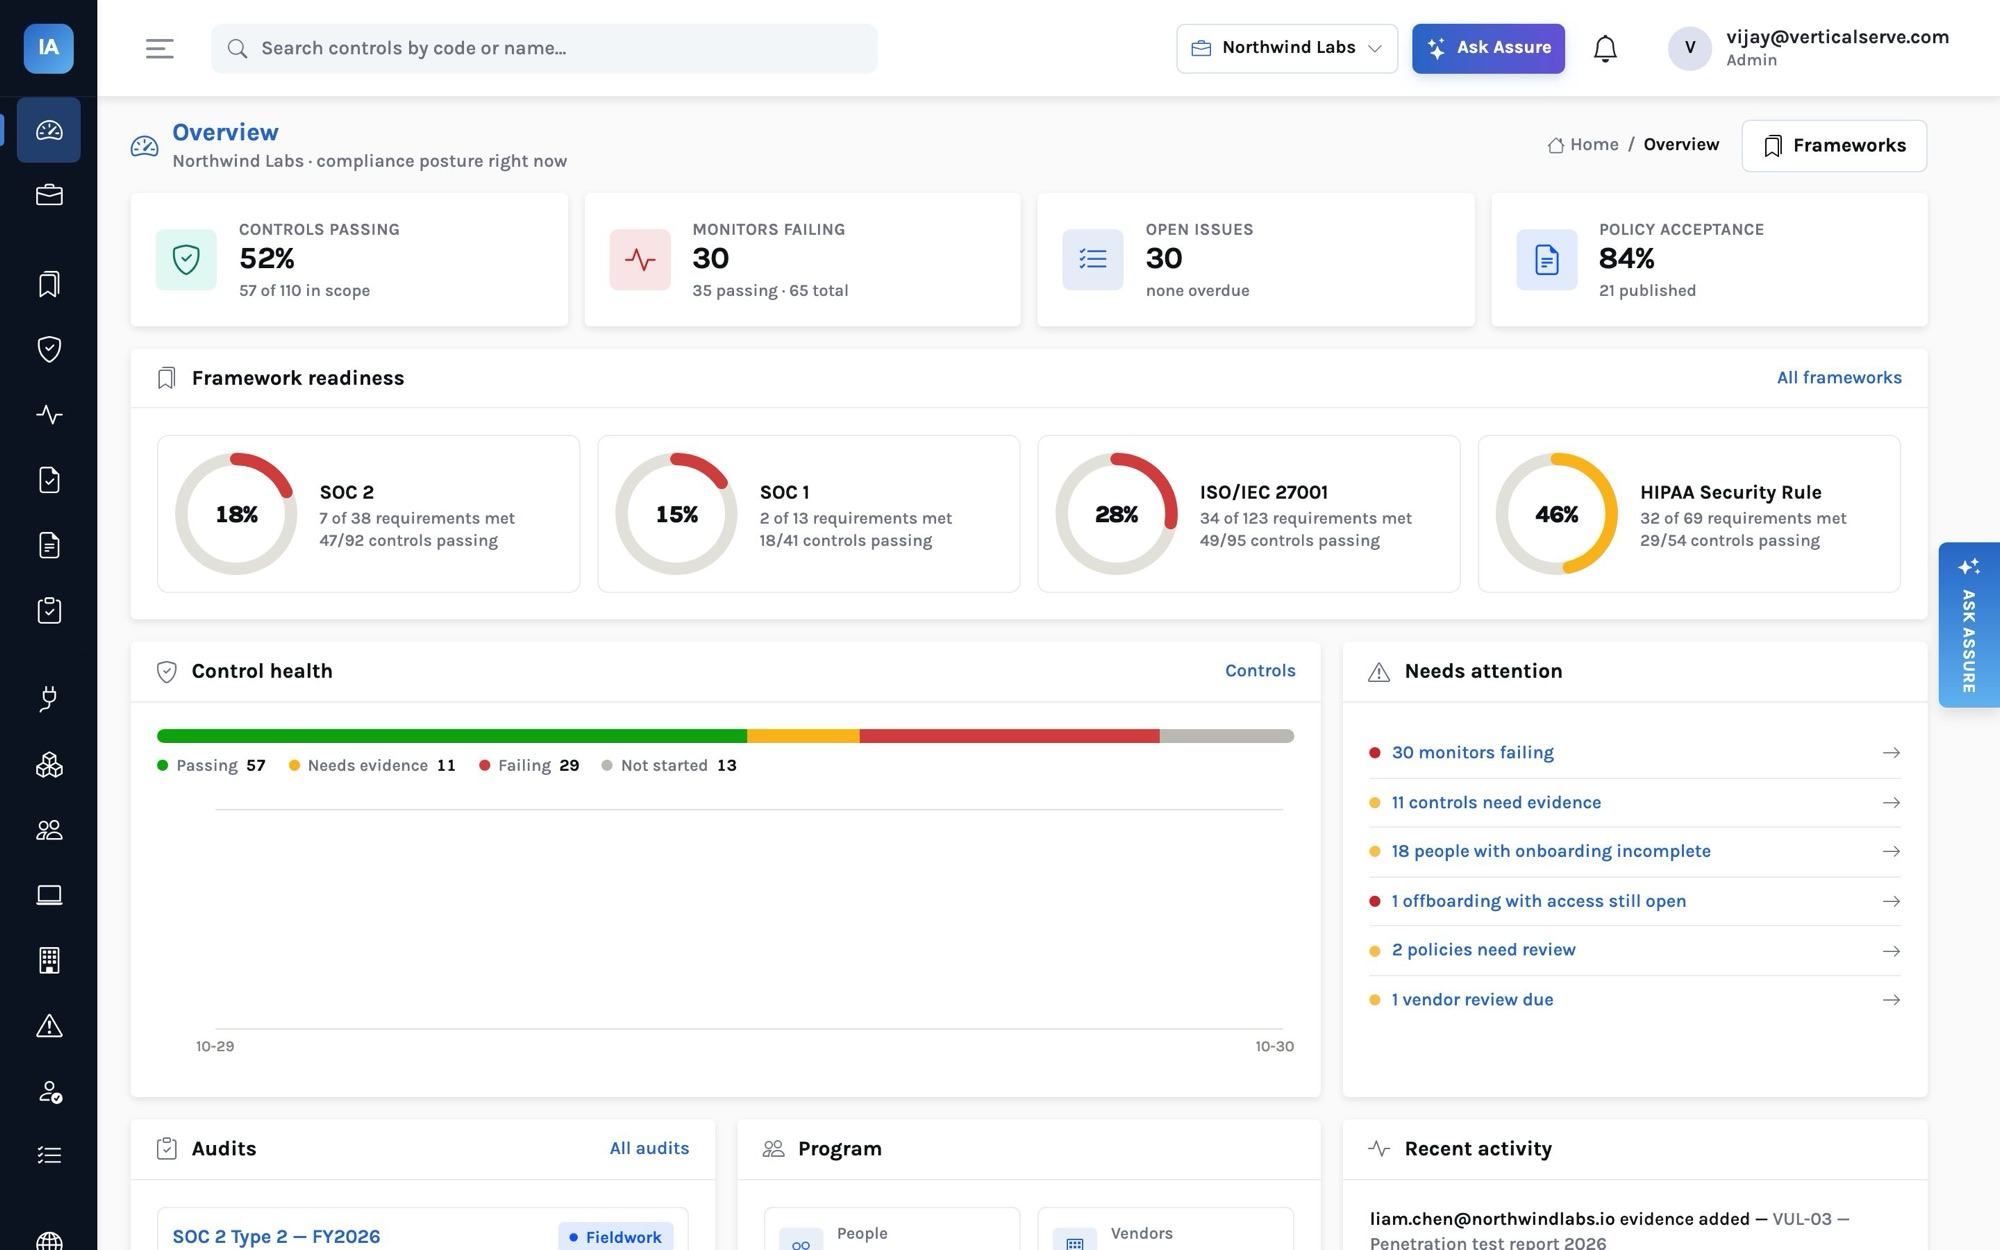
Which client is furthest from audit-ready?Portfolio, by readiness
Which clients have critical issues open?Portfolio’s issue counts
Which audits are in fieldwork this month?Portfolio’s audits in flight
Switch to a clientThe workspace switcher
Who in the client can approve policies?The client’s users and roles
Give the client’s auditor accessThe audit’s Auditors tab
Outcomes
What teams do with it
One login, many programs
The same email, a role in each client.
Clients kept apart
Scoping in code and row-level security underneath.
Repeatable onboarding
Frameworks, policies, risks and answers in one step.
Where it stops. The portfolio is a SaaS feature; a self-hosted install is one organization. VerticalServe runs programs and prepares evidence; reports are issued by independent licensed CPA firms.