- contact@verticalserve.com
- Continuous compliance, proven every hour

Policies & training
Policies people actually accept
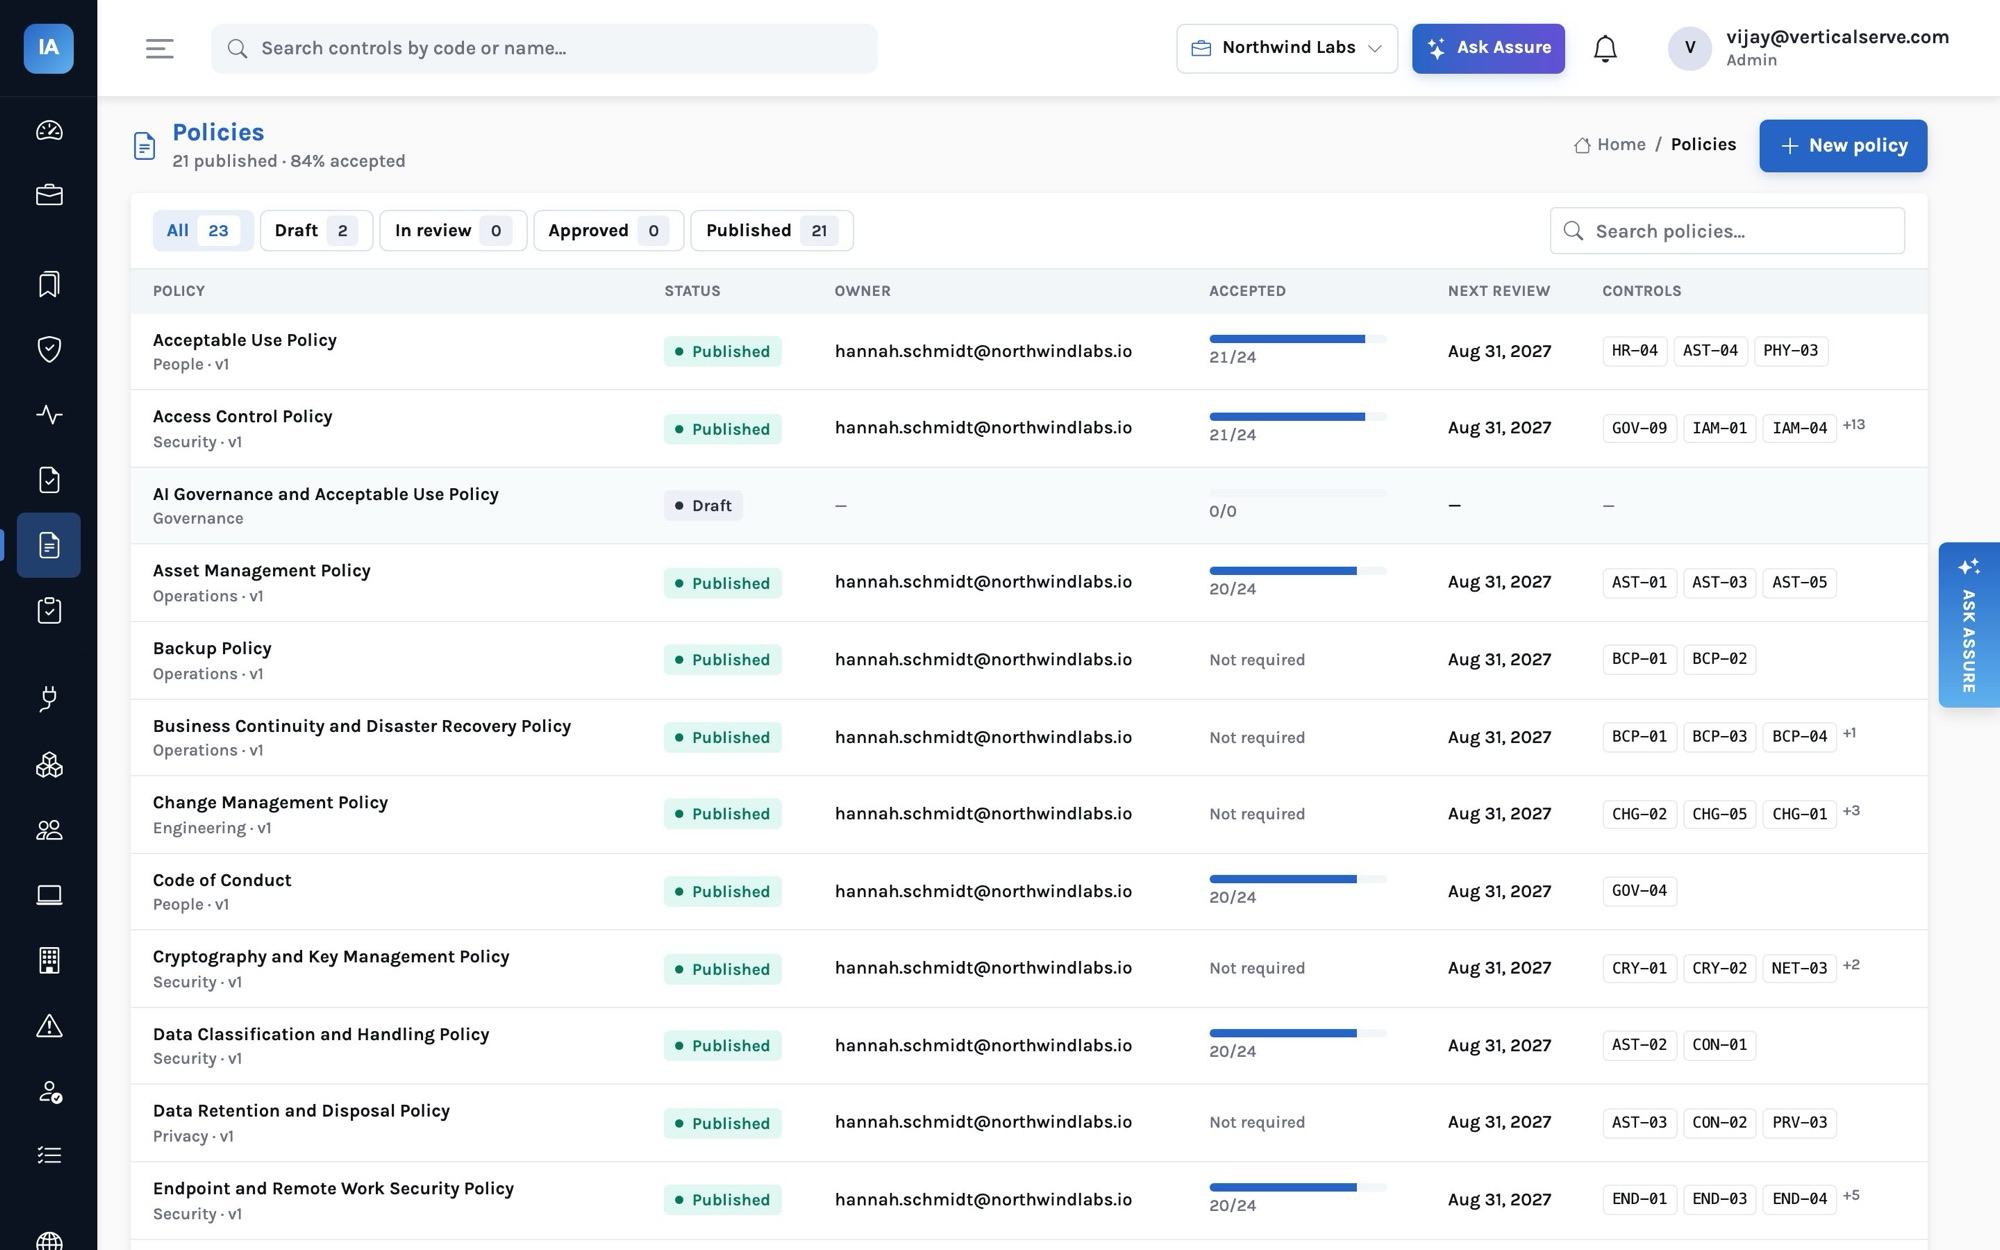
Start from twenty-three templates written for SOC 2 and ISO 27001, edit them in markdown, approve and publish with every version kept, and track acceptance of the version in force.
Templates
Twenty-three policies an auditor will recognise
Information security, acceptable use, access control, asset management, data classification, retention and disposal, cryptography, network, endpoint and remote work, logging and monitoring, vulnerability and patch management, secure development, change management, backup, business continuity, incident response, risk, vendor, HR security, physical security, privacy, code of conduct, and AI governance.
Each is filled with your company name, security contact and dates, and states concrete requirements consistent with the controls that cite it: MFA everywhere, 90-day key rotation, vulnerability SLAs, quarterly access reviews, offboarding within 3 business days, an annual restore test and tabletop.
Lifecycle
Draft, review, approve, publish
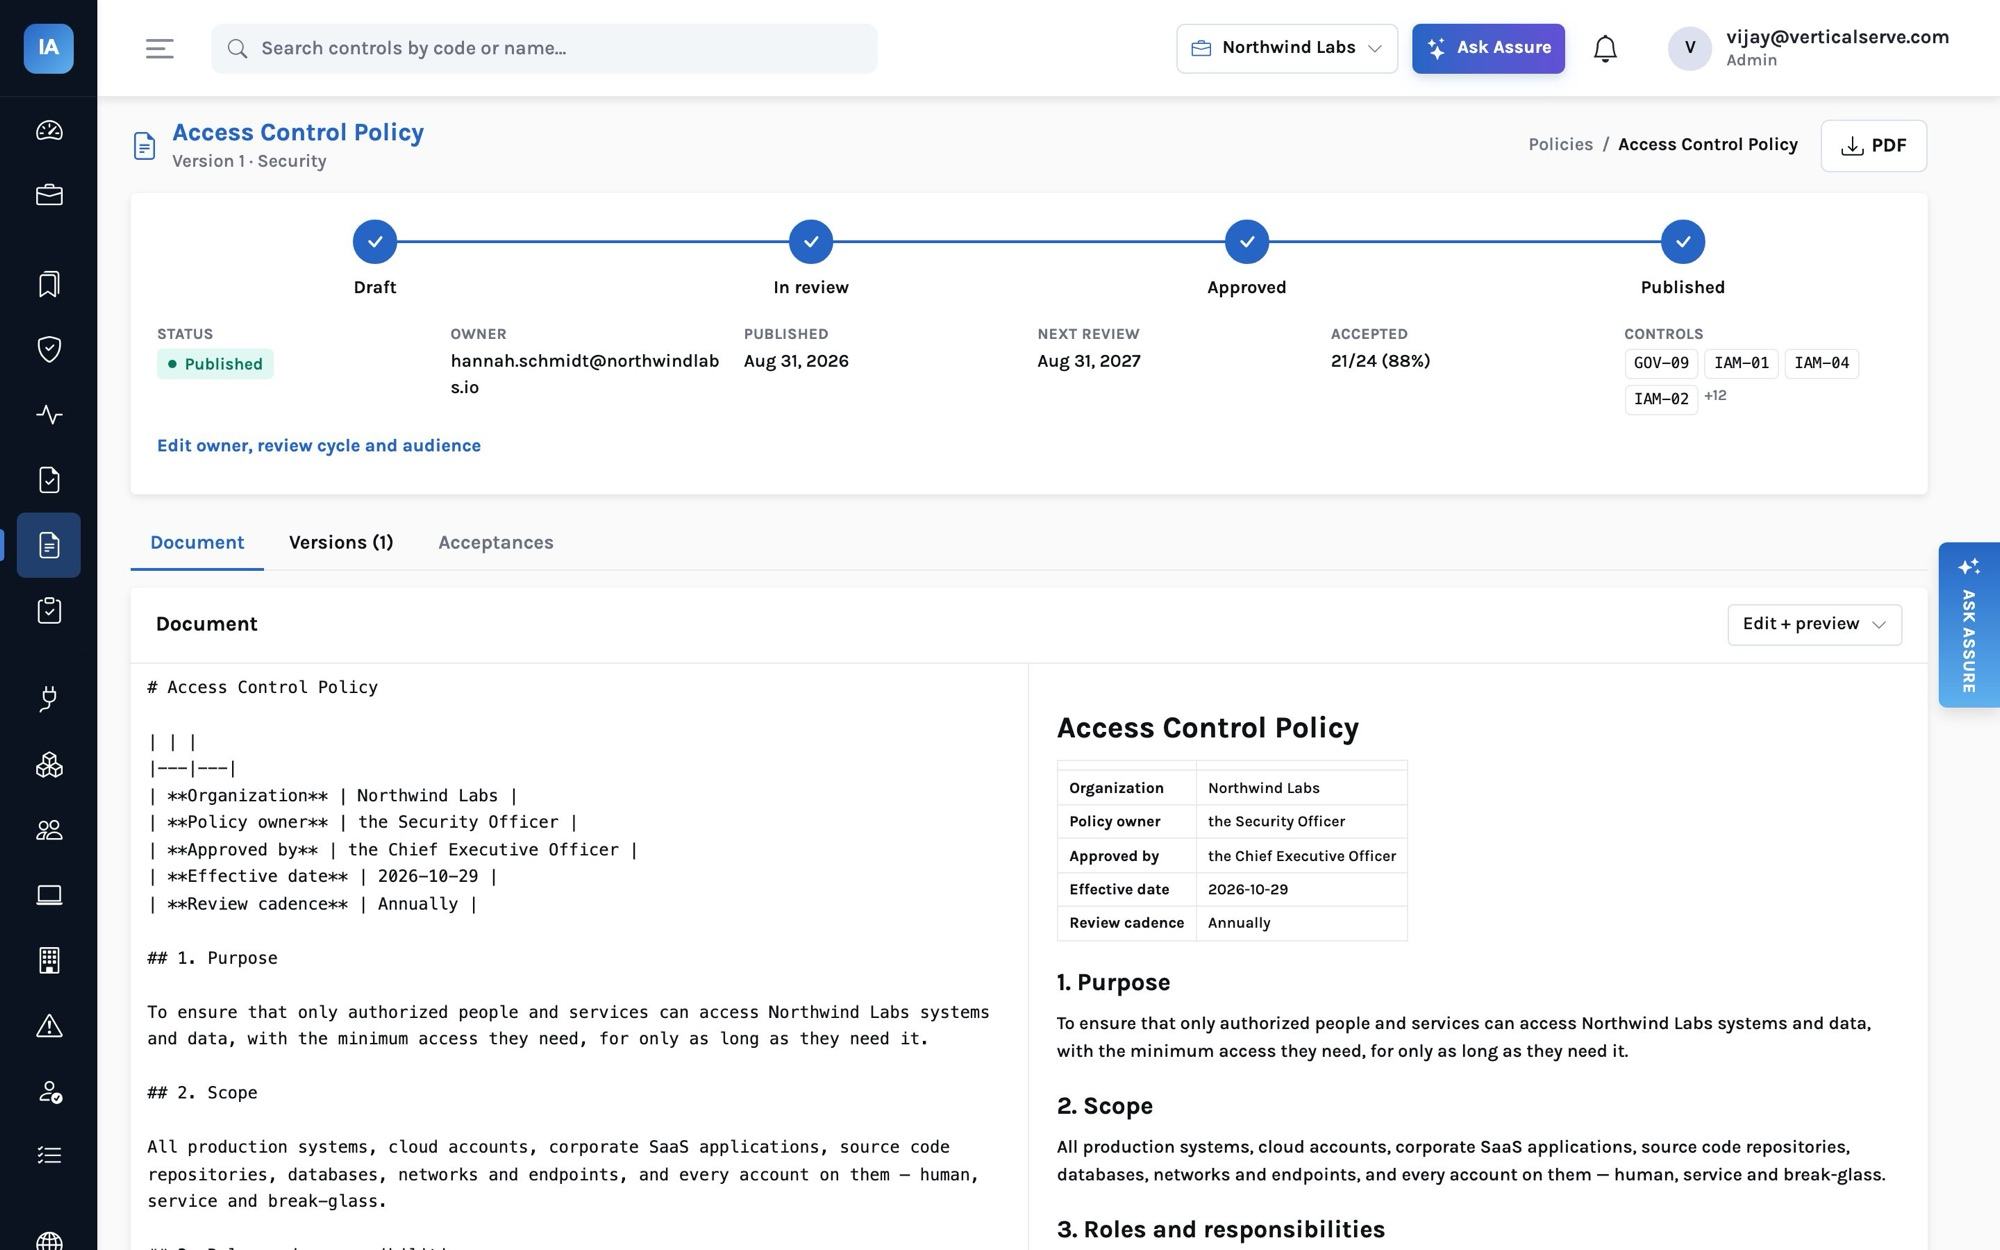
Edit in markdown with a live preview. Submit for review, approve, publish: the approved version comes into force, the previous one is superseded, the next review date is set from the policy’s cycle, and personnel are asked to accept. A published version stays in force while the next is drafted.
- Every version kept, with who approved it and when
- Acceptance per version, so a new version restarts it
- A PDF of any version, with the approval line
- A published policy is retired, never deleted: its acceptances are evidence
- Draft with AI from a template and instructions; with no model, the template itself
Training
Five built-in courses
Each has sections to read and a quiz; 80% passes, and a pass is recorded with the score. KnowBe4 completions count too.
| Course | Who |
|---|---|
| Security awareness | Everyone, annually: phishing, passwords and MFA, device security, data handling, reporting incidents |
| Secure coding | Engineers: OWASP Top 10, secrets, dependency hygiene, code review |
| HIPAA privacy and security | People handling health information |
| PCI DSS awareness | People near card data |
| AI acceptable use | Everyone using AI tools |
How it works
A policy from template to accepted
Questions it answers
What you can find out
Each one is answered on a screen you can open, and most can be typed into Ask Assure as they are.
Which policies are overdue for review?Policies are approved, published and reviewed within a year
Who has not accepted the current access policy?The policy’s acceptances tab
Which controls rely on this policy?The policy’s linked controls
What changed between versions?The versions list with change summaries
Who passed security awareness this year?Training completions, and the people page
Print the policy for the auditorPDF of the published version
Outcomes
What teams do with it
A policy set in a day
Twenty-three templates adopted at once, then edited.
Acceptance without chasing
Reminders from the bell; the employee portal does the rest.
Review dates that come round
The review cycle sets the next date; overdue fails a monitor.
Where it stops. Templates are a strong starting point, not legal advice: edit them to match how you actually operate, because the auditor tests what the policy says. Acceptance is a click-through with the time, IP address and browser recorded; there is no e-signature integration.