- contact@verticalserve.com
- Continuous compliance, proven every hour

InsightAssure · continuous compliance
Continuous compliance, proven every hour
InsightAssure connects read-only to the systems you already run (cloud, identity provider, HR, source control, laptops, scanners) and tests your controls every hour. SOC 2, SOC 1, ISO 27001, HIPAA, PCI DSS, NIST CSF, GDPR and ISO 42001 are reported from one control set. Your auditor works in a scoped workspace, and customers see the live status on your Trust Center. Run it as VerticalServe SaaS or in your own cloud.
8frameworks, 559 requirements mapped
114unified controls, tested once, reported everywhere
65automated tests, every hour
55read-only integrations, plus a push API
Proof, not promises
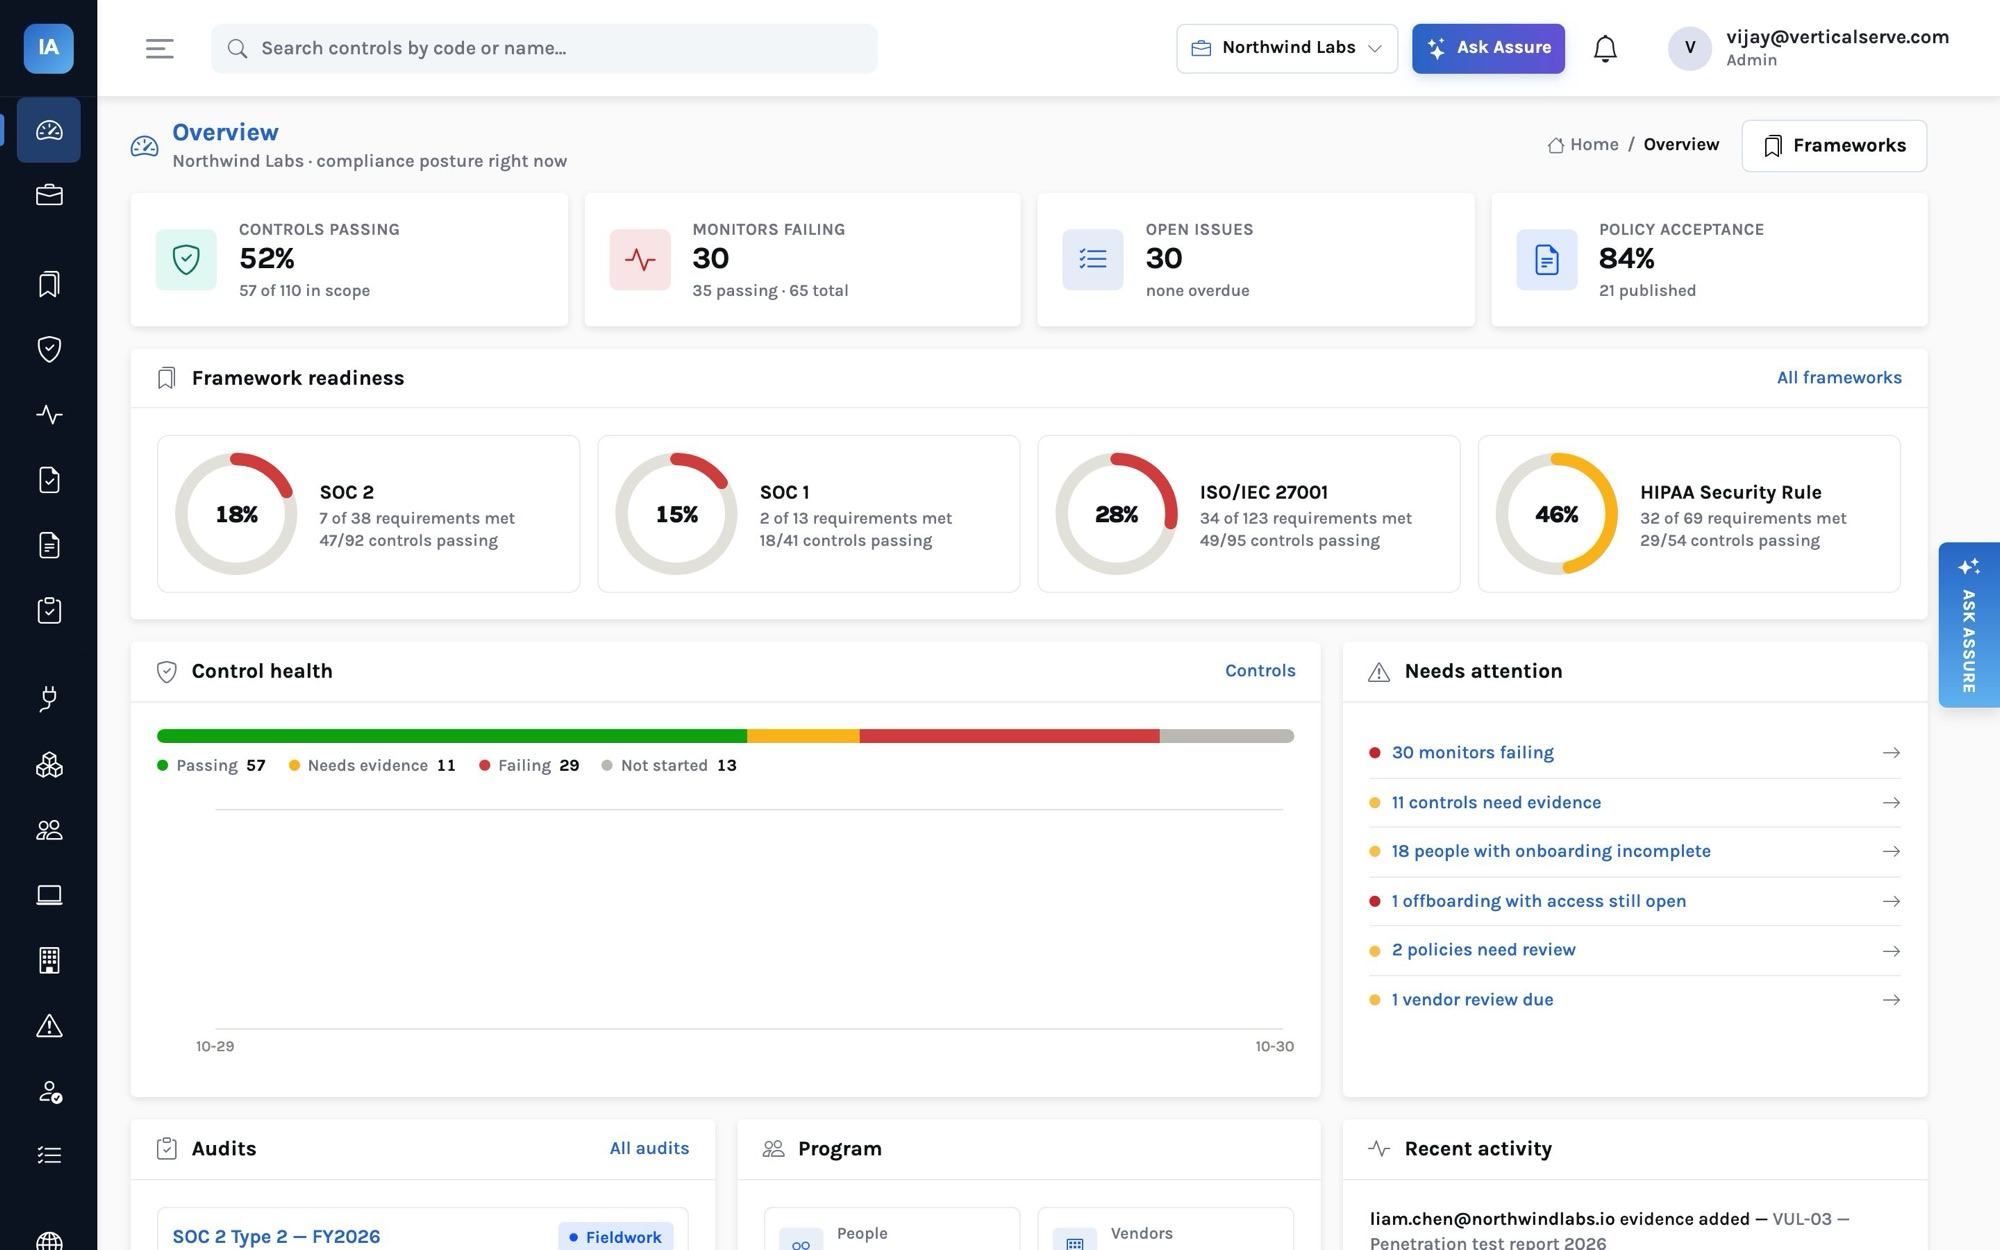
Three screens from the demo company, as they are
Northwind Labs is a 25-person demo company with real gaps planted in its systems: an engineer who left but kept his accounts, a public bucket, unreviewed changes. This is what InsightAssure found without being asked.
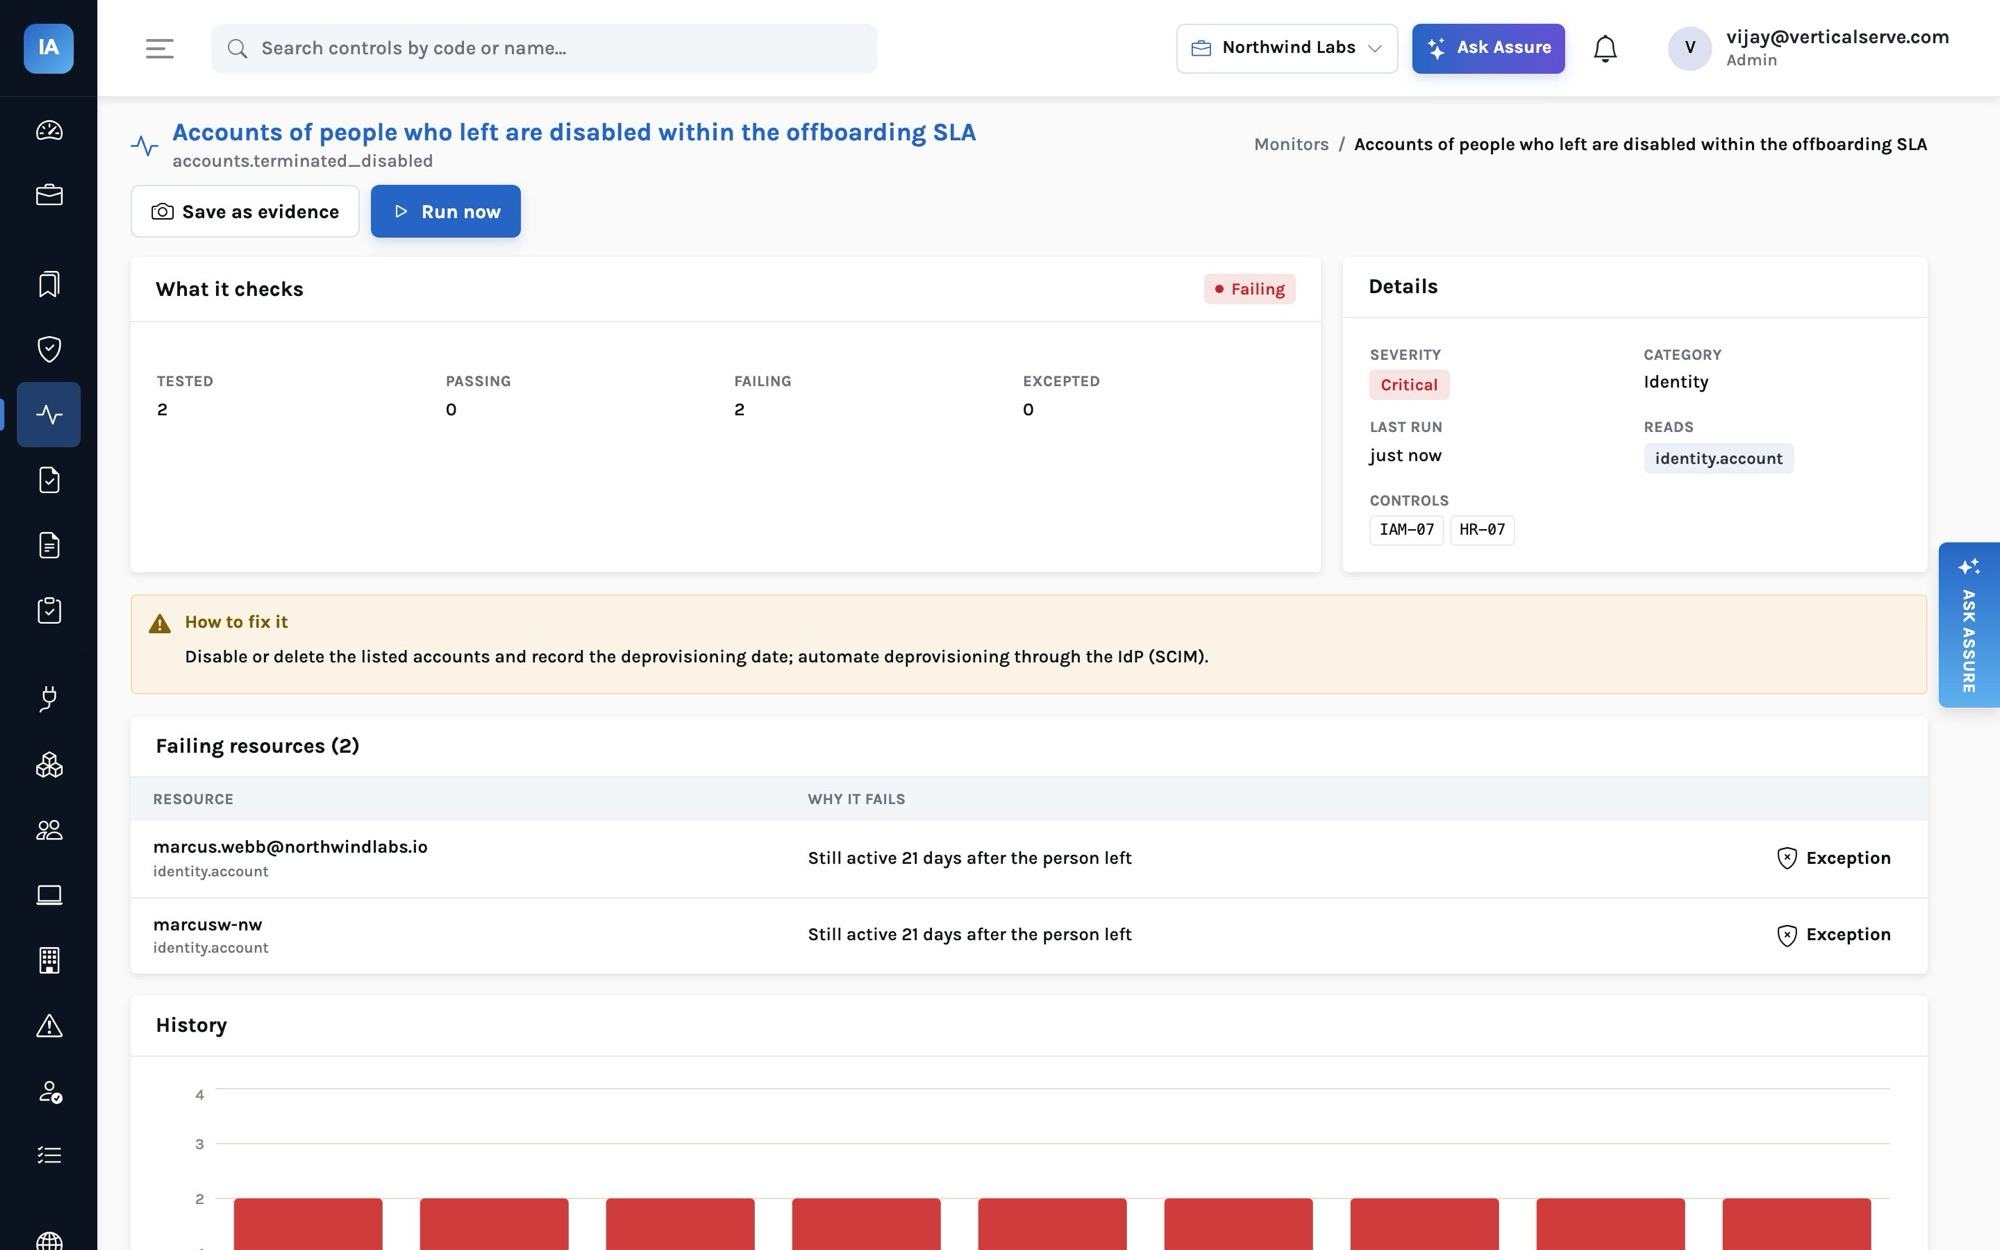
The leaver, by name
Marcus Webb left 21 days ago. The offboarding monitor found his Okta and GitHub accounts still active, named both, and said how to fix it.
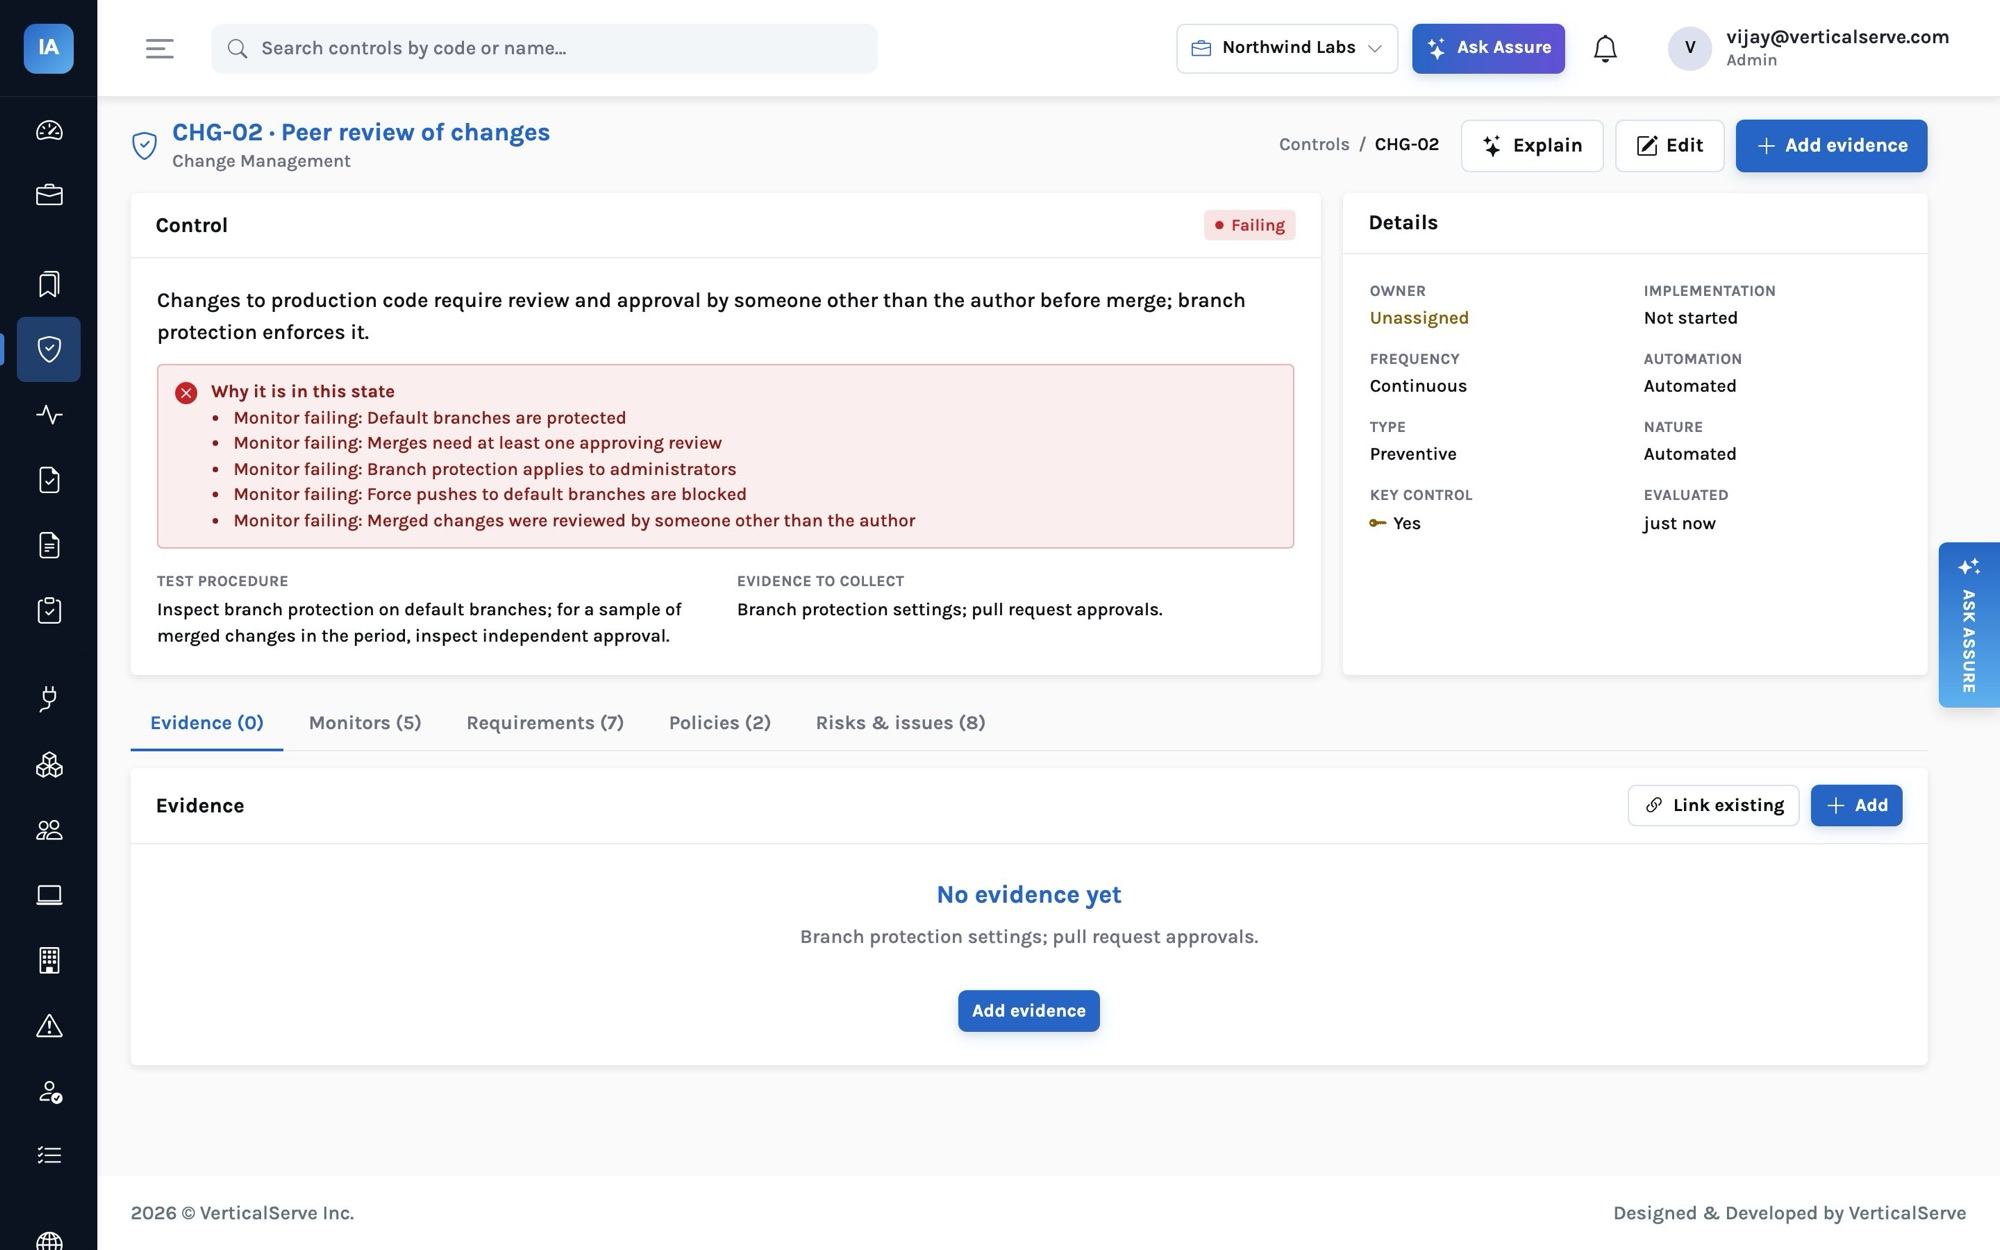
Why a control fails
CHG-02 Peer review of changes is failing because five tests over the GitHub data fail, and the auditor’s test procedure sits right beside them.
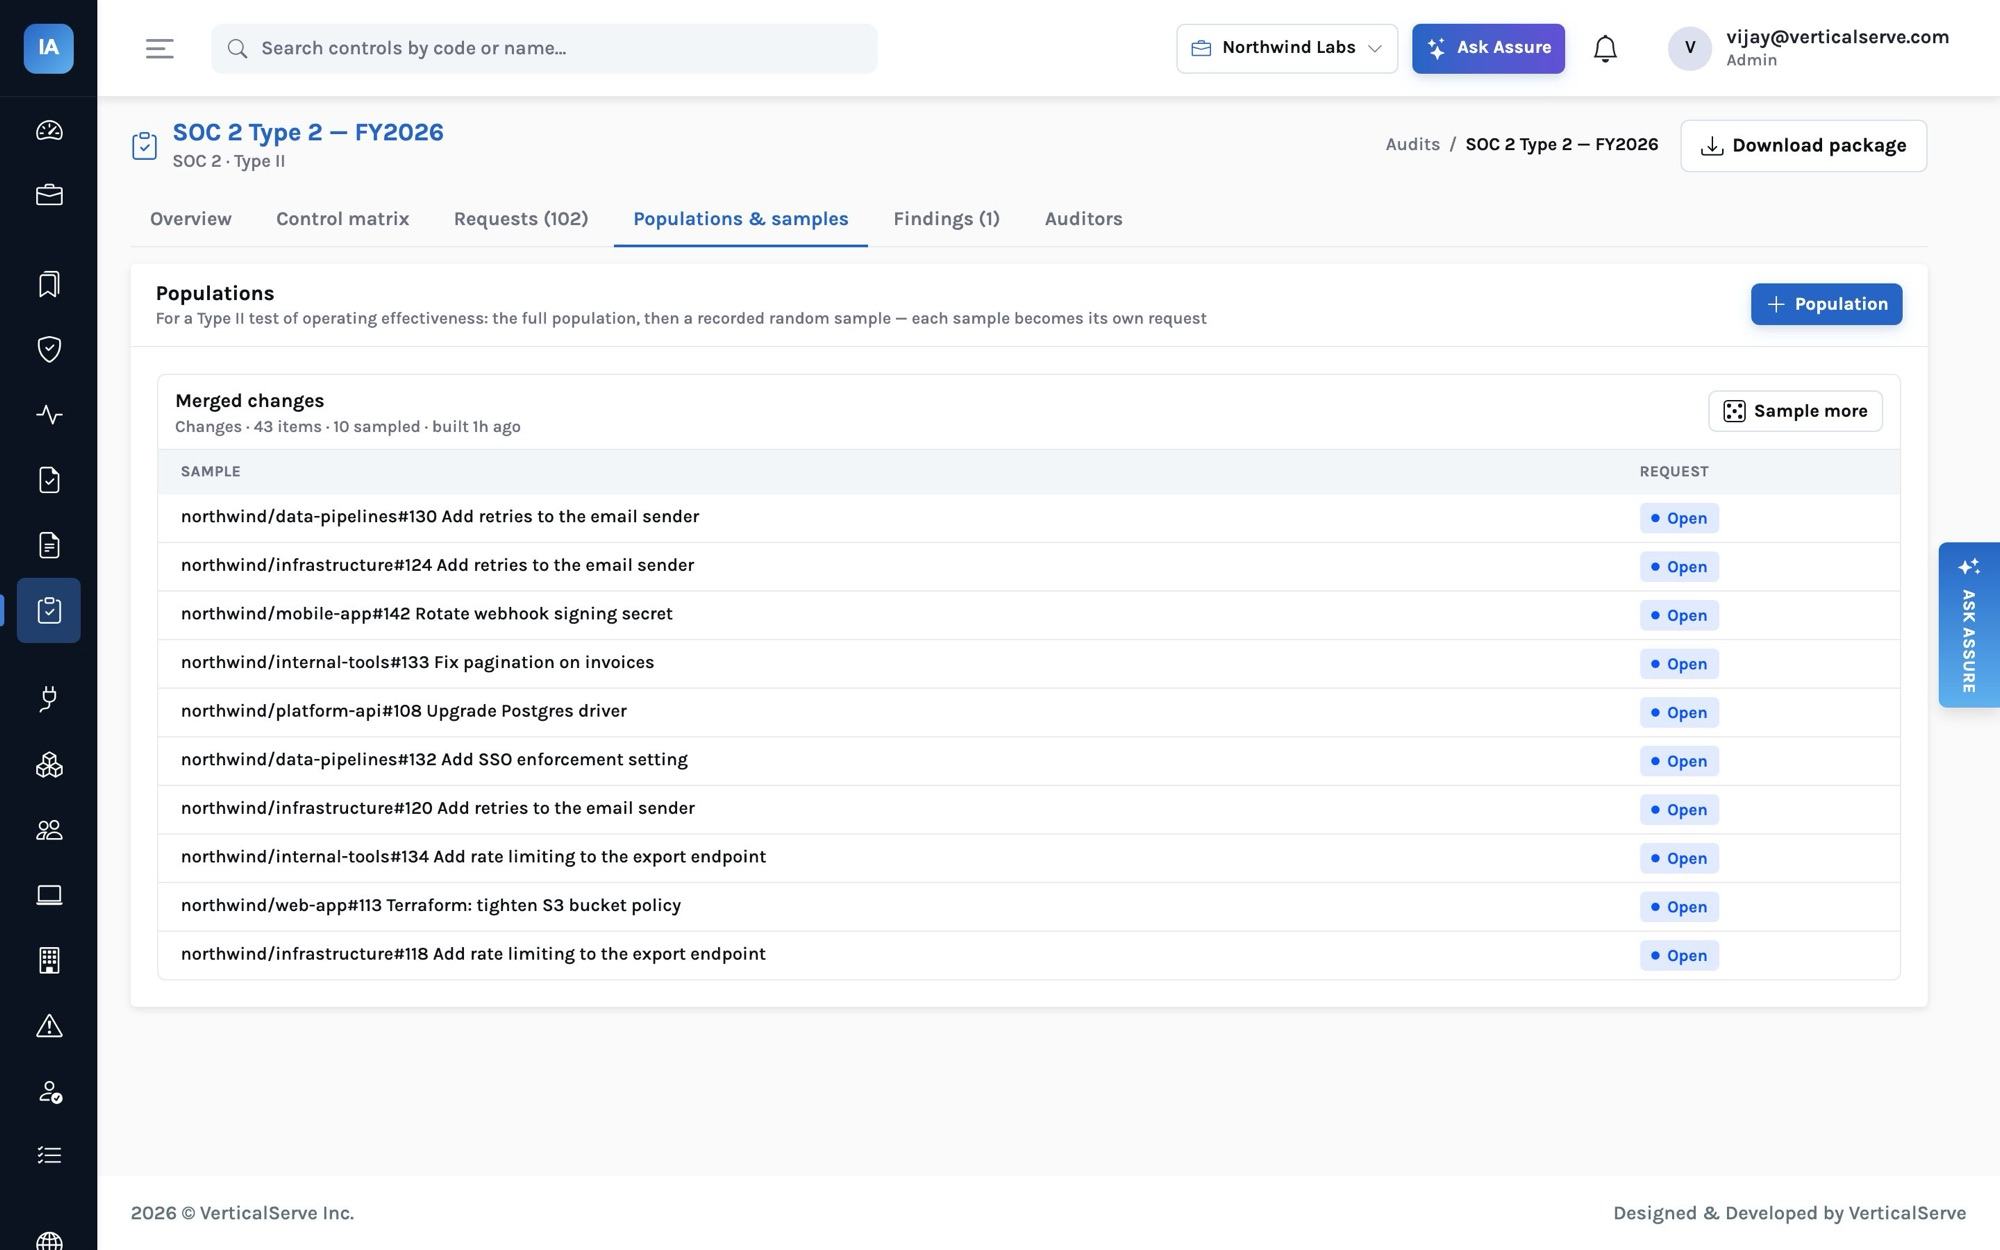
An audit that samples itself
The auditor drew 10 of 43 merged changes with a recorded seed; three lacked a second reviewer and became a finding.
What continuous means here
Six rules the product is built on
Every compliance tool says “automated”. These are the properties that decide whether an auditor, and a customer, can rely on what it says.
Tested, not attested
Controls take their health from monitors over real data and from evidence collected inside each control’s frequency window. A checkbox nobody verified does not turn a control green.
Not judged when not reported
A monitor never fails a resource for data its source did not provide. An unknown MFA status is unknown, not a pass and not a failure, and the monitor says when it has no data.
One control, every framework
114 unified controls cover 559 requirements across eight frameworks. MFA is tested once and counts toward SOC 2 CC6.1, ISO A.8.5, HIPAA 164.312(d) and PCI DSS 8.4.
Evidence an auditor can reproduce
Monitor history, access-review decisions and policy acceptances are kept as evidence. Samples are drawn with a seed stored on the audit, so the same draw can be made again.
Honest AI
Questionnaire answers come from your approved answers, published policies and the live health of the controls behind them. A failing control is never described as in place.
Yours to run
VerticalServe SaaS, or the same images in your own cloud with your Postgres, object store and model provider. With no model at all, every AI feature still answers by rule.
The product
Everything a compliance program needs, from one control set
Frameworks, monitoring, people, policies, vendors, risk, access reviews, audits and trust, built around one set of controls so nothing is collected twice.
Frameworks & controls
Eight frameworks and 559 requirements mapped to 114 unified controls. Test a control once; its health counts toward every framework that asks for it.
Learn moreContinuous monitoring
Sixty-five automated tests run hourly over a normalized inventory. A failure names the resource and the fix, opens an issue, and closes it when it passes again.
Learn moreIntegrations
Fifty-five read-only connectors across cloud, identity, HR, code, devices, scanners, ticketing and monitoring, plus CSV import and a push API.
Learn morePeople & devices
Personnel from your HR system, onboarding checked automatically, offboarding checked against every system, and laptop posture from MDM or a small agent.
Learn morePolicies & training
Twenty-three audit-ready policies with versions, approval and acceptance, and five built-in training courses with quizzes.
Learn moreVendors & risk
Vendor inventory, SOC report reviews that map CUECs to your controls, SaaS discovery from the IdP, and a 47-risk register with a 5×5 heat map.
Learn moreAccess reviews
Quarterly reviews from any identity system, with accounts flagged for leavers, admins, no MFA and inactivity; the decisions become evidence.
Learn moreAuditor workspace
Requests generated from your controls, an auditor role scoped to one audit, seeded reproducible sampling, findings and a one-click package.
Learn moreSOC 1
Control objectives as editable rows, CUECs and CSOCs in the system description, subservice organizations carved out and monitored.
Learn moreTrust Center
A public page with live control status, subprocessors and NDA-gated documents released through expiring links.
Learn moreAI questionnaires & Ask
Questionnaires answered from your approved answers, policies and live control health, with citations, and plain-language answers about your own program.
Learn moreFor consultancies
A workspace per client, consultant roles in each, and a portfolio of every client’s readiness in one view.
Learn more
How a control is proven
From a connected system to a met requirement
Each step can be opened and checked: the resource, the test result, the control’s reasons, the requirement it satisfies.
Solutions
Who it is for
The same product, scoped for the report your customers or regulators ask for.
Runs where your data lives
VerticalServe SaaS, or your own cloud
The same images either way. Self-hosted, InsightAssure uses your Postgres, your object store and your secret manager, and any model provider or none.
SaaSHosted by VerticalServe; a workspace per organization with Postgres row-level security between tenants
AWSRDS PostgreSQL, S3, Secrets Manager, Bedrock; the AWS integration reads accounts through an assumed role
AzureDatabase for PostgreSQL, Blob Storage, Key Vault, Azure OpenAI
Google CloudCloud SQL, Cloud Storage, Secret Manager, Vertex AI
On-premises
./install.sh and Docker Compose on one VM; no model required
From the blog
Playbooks and worked examples
SOC 2, SOC 1, monitoring and audits, shown on the demo company’s real data.
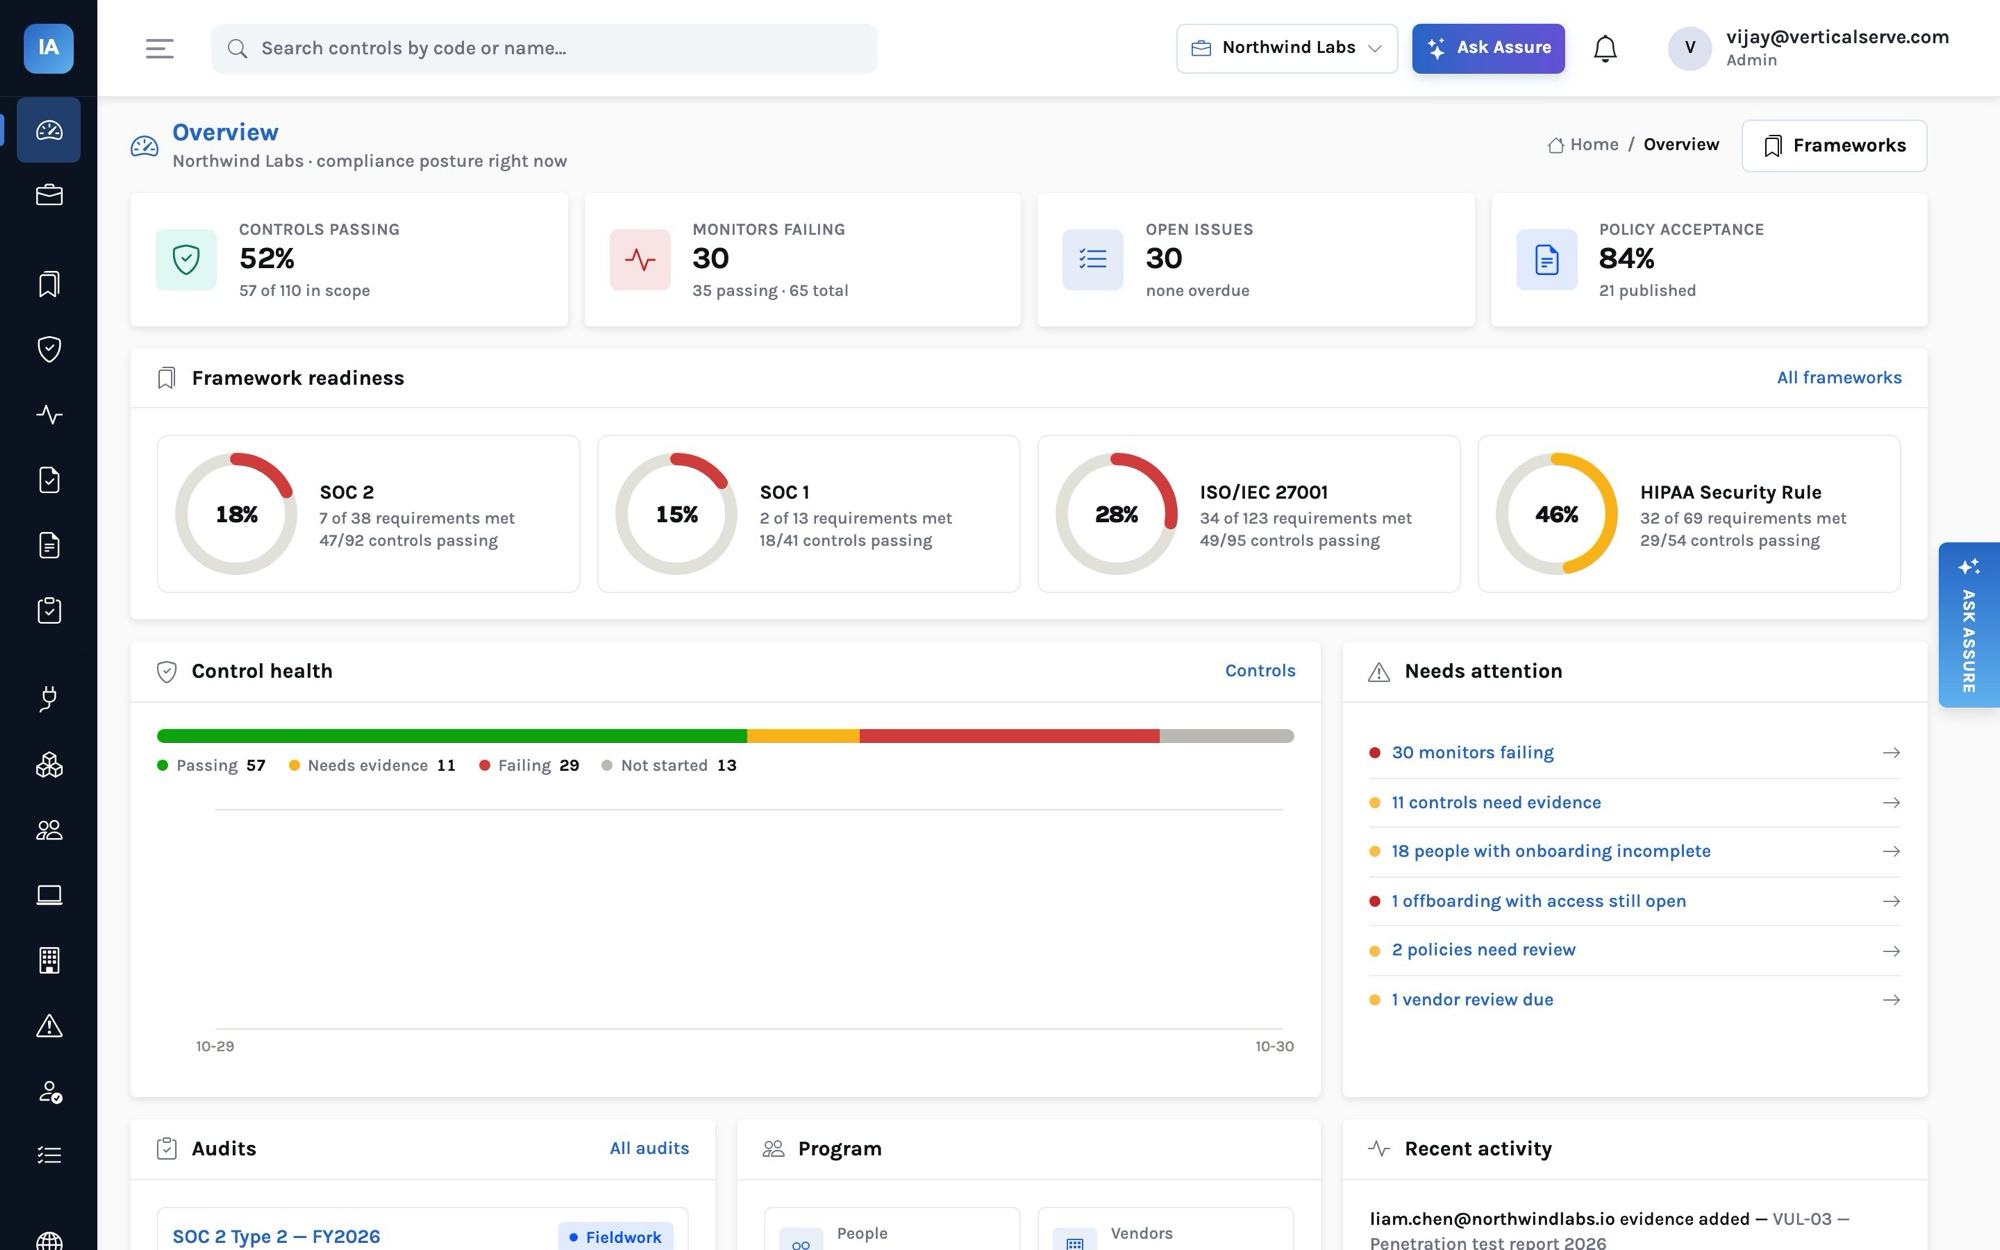
SOC 2
SOC 2 in 90 days — a practical playbook for a small SaaS team
Scope, readiness week by week, Type 1 vs Type 2, the observation period and fieldwork — a SOC 2 plan a 25-person SaaS company can actually run.
Read article
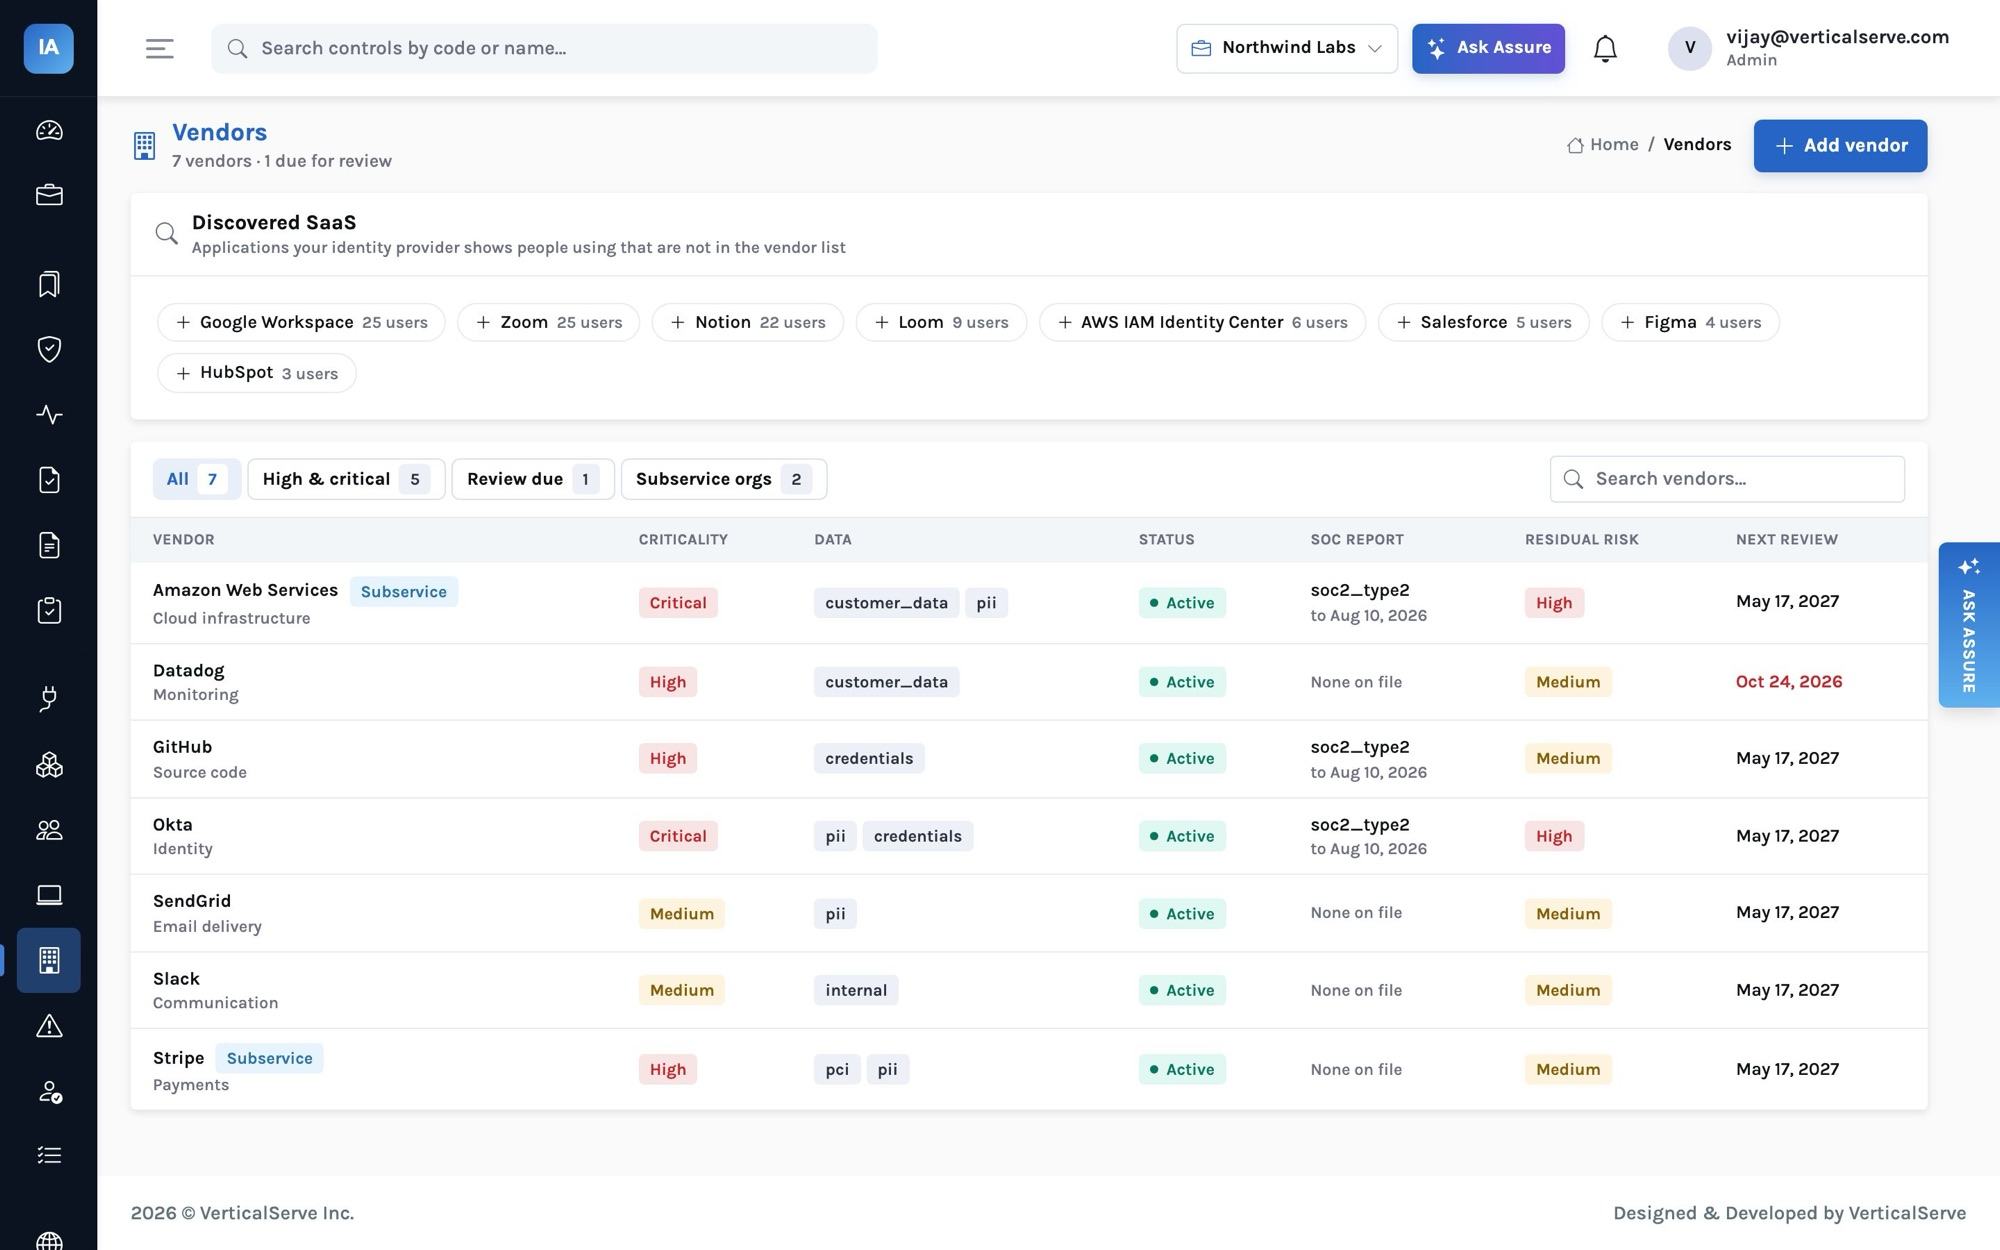
SOC 1
SOC 1 explained properly — control objectives, CUECs, CSOCs and carve-outs
How SOC 1 differs from SOC 2, how to write control objectives, and how CUECs, CSOCs and carved-out subservice organizations fit together.
Read article
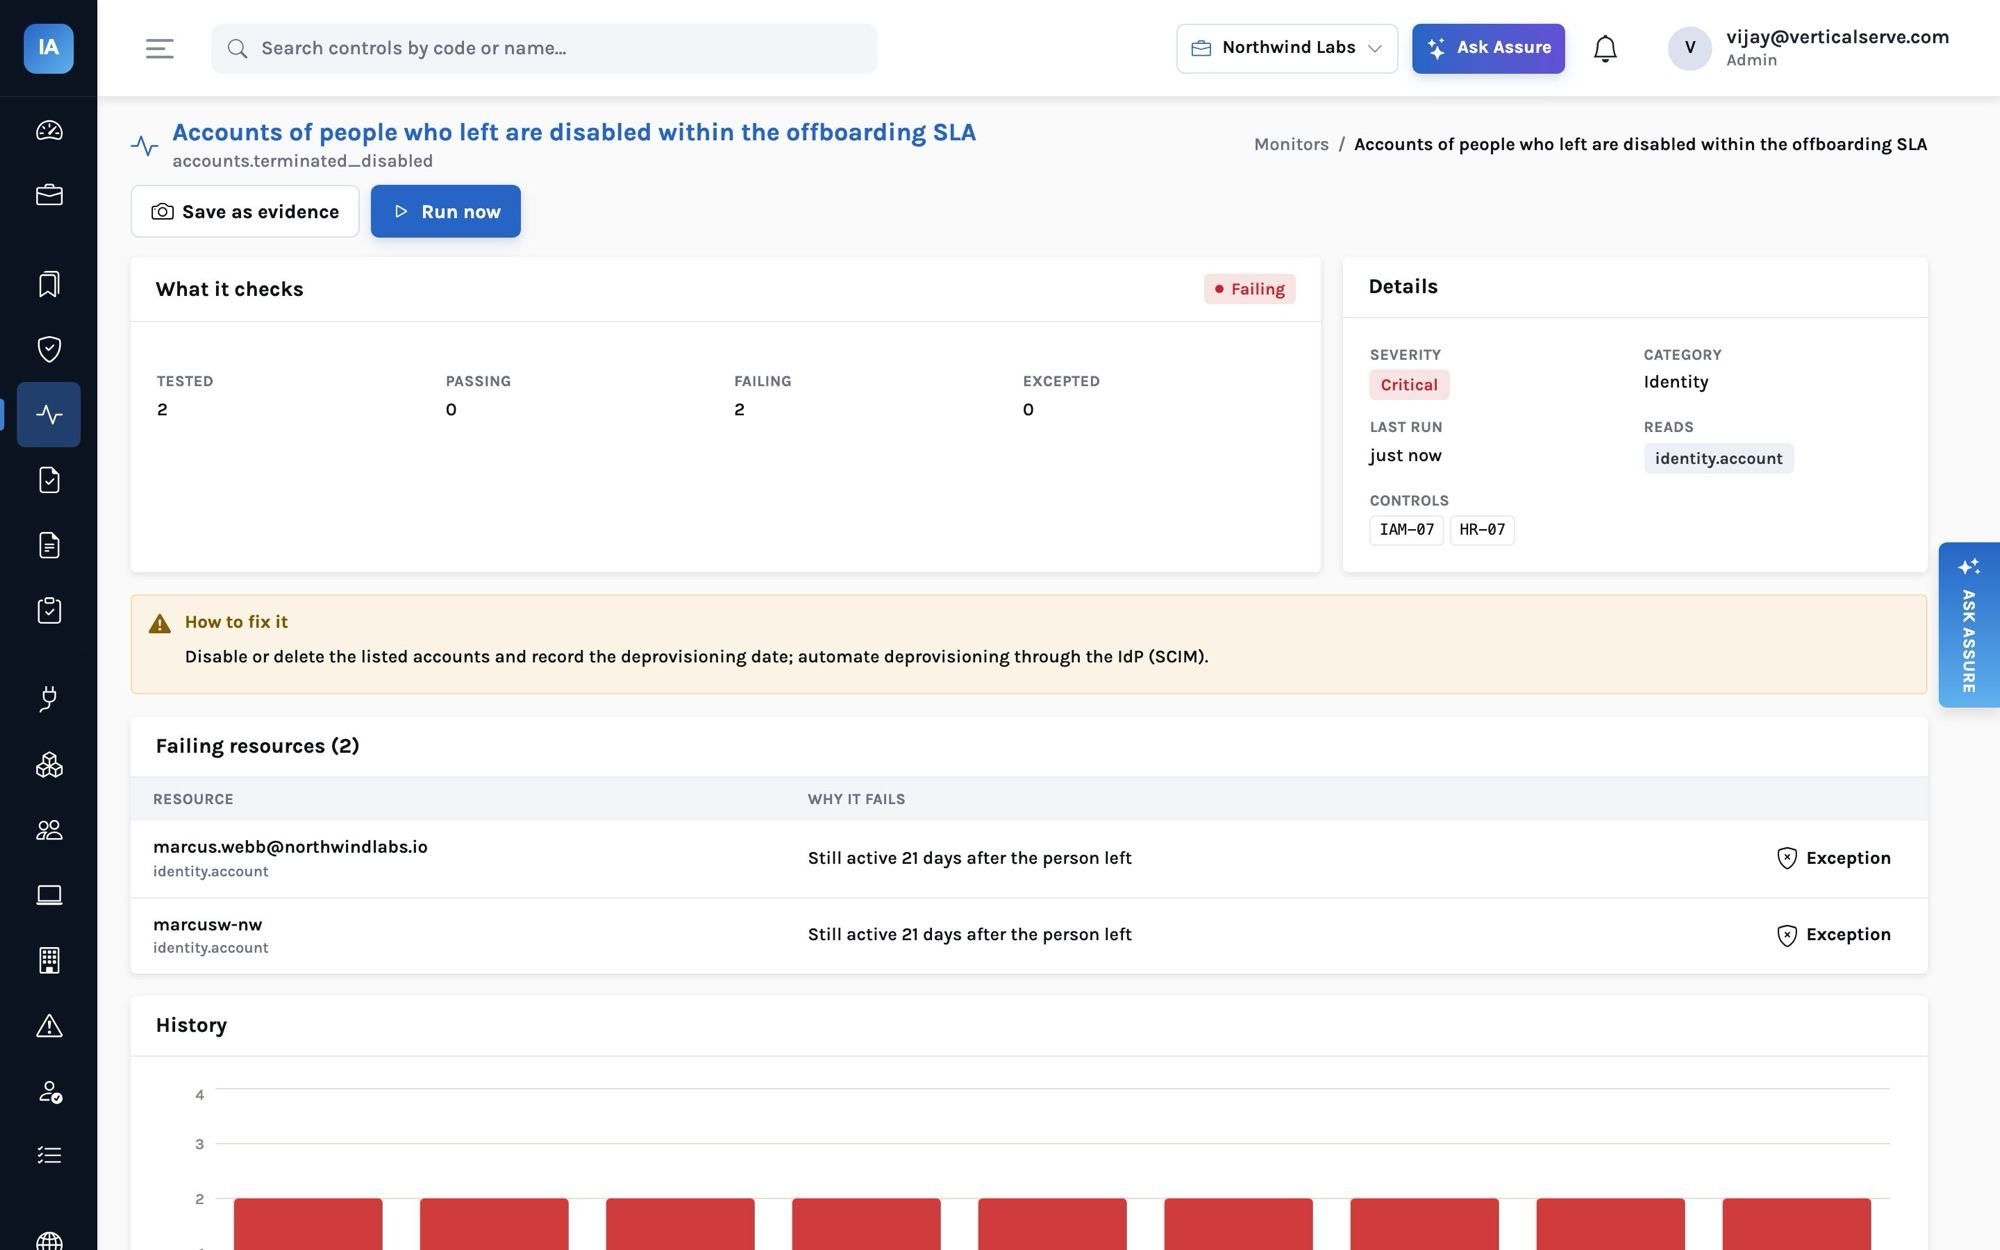
Monitoring
How continuous control monitoring actually works
From an Okta account to a framework readiness score — the data model, the 65 monitors, exceptions and the rule that keeps tests honest.
Read article